GRC software.
Governance, risk & compliance, unified.
GRC software (governance, risk and compliance software) is a platform that manages an organisation's policies, risks, controls, obligations, audits and actions in one connected, auditable system, instead of spreadsheets and separate tools. XGRC® is an integrated GRC platform that adds ESG and data protection on the same foundation, giving your organisation a single version of the truth.
One platform. One source of truth.
Most organisations run governance, risk, compliance, and ESG in isolation: separate tools, disconnected data, duplicate effort. XGRC® consolidates every discipline into one foundation, so decisions are based on the same data, controls link to the right risks, and your compliance status is always current.
One source of truth
Six disciplines. One foundation.
Policy, Governance & Board Reporting
Manage policies, document controls, board reporting, and stakeholder oversight from a single governance hub.
Explore → RiskEnterprise Risk Management
Identify, assess, and treat enterprise risk using a consistent framework aligned to ISO 31000 and COSO.
Explore → ComplianceCompliance & Regulation
Track obligations across ISO standards, GDPR, POPIA, PAIA, and industry regulations with real-time compliance status.
Explore → Data ProtectionData Protection & Privacy
Manage GDPR and POPIA obligations, data subject access requests, privacy impact assessments, and data breach response.
Explore → AssuranceInternal Audit & Assurance
Plan, execute, and manage the full internal audit lifecycle, linked to risks, controls, and corrective actions.
Explore → ESGESG, Safety & Operations
Collect and report ESG data, manage safety incidents and inspections, aligned to ISO 45001, ISO 14001, and GRI.
Explore →What a GRC platform does, day to day.
Whichever discipline you start with, GRC software solutions do the same core jobs. In XGRC® each one runs on the same data, so a risk links to its controls, its obligations, its audit findings and its corrective actions without double entry.
Risk management
Risk registers, likelihood and impact scoring, risk appetite thresholds, key risk indicators and treatment plans, aligned to ISO 31000 and COSO.
Enterprise risk management software →Compliance obligations
Obligations across ISO standards, GDPR, POPIA, PAIA and industry regulations with real-time compliance status, plus jurisdiction-specific regulatory intelligence from Libryo.
Regulatory compliance →Policies and governance execution
XLOGIC® converts policies, frameworks, controls and obligations into structured workflows with accountability, evidence capture and auditability.
XLOGIC® →Audit and assurance
Risk-based internal audit planning, fieldwork, findings and a combined assurance matrix that maps every assurance provider to the risks they cover.
Integrated Assurance →Incidents and corrective actions
Incidents, inspections and non-conformances captured in the field, including offline in the SHEQX® iOS and Android apps, with corrective actions assigned and tracked to closure.
SHEQX® →Reporting, evidence and governed AI
Executive dashboards and board reporting from live data, an audit trail behind every record, and MAIA® governed AI with a full AI interaction audit trail.
Take the live tour →Real dashboards. Real decisions.
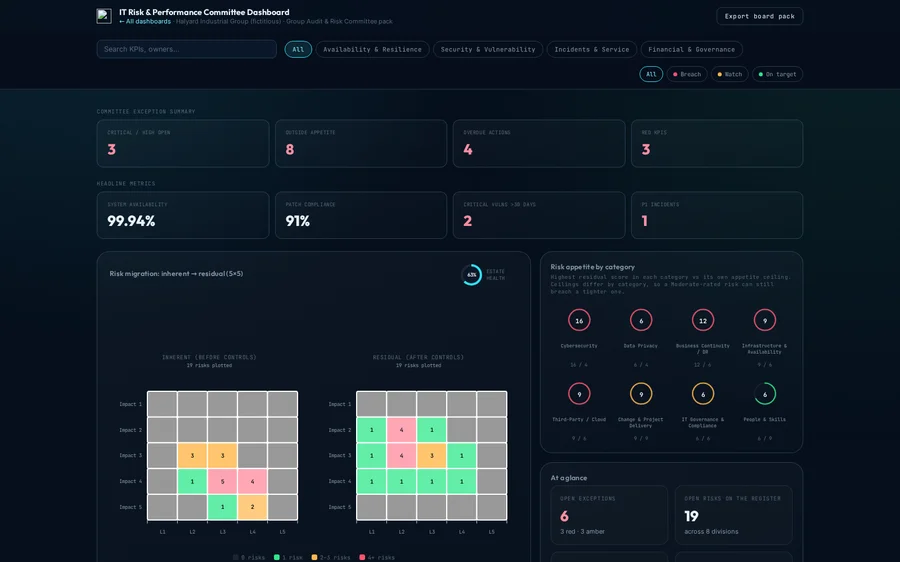
Every discipline has a dedicated intelligence layer, executive dashboards built for decision-makers, not data analysts. These are live, click-through demonstrations, not screenshots.
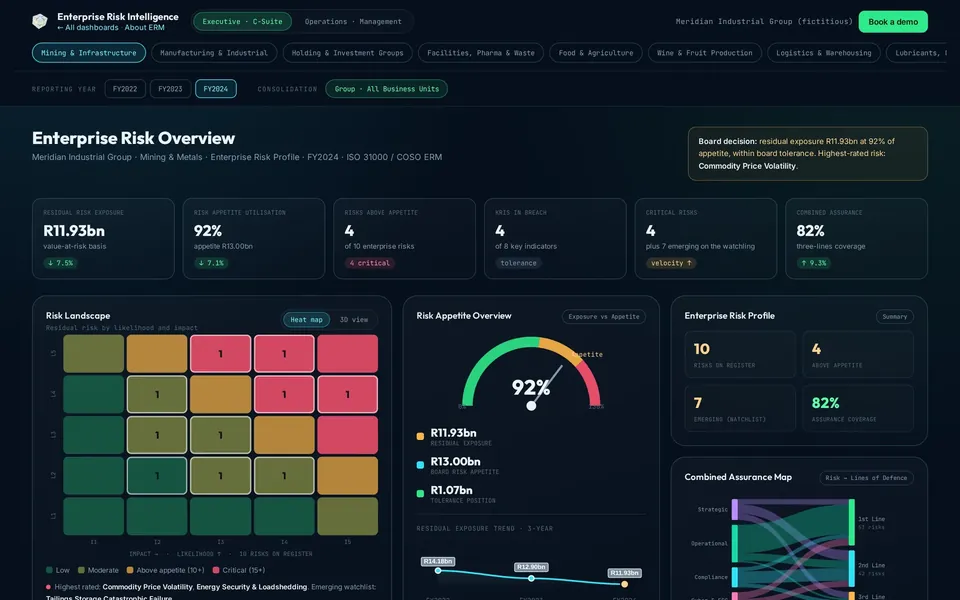
Illustrative data. See all 17 live dashboards →
Built for global standards and local law.
XGRC® supports the frameworks your organisation must comply with, from international ISO standards to South African legislation.
- GDPR
- ISO 27001
- ISO 9001
- ISO 14001
- ISO 45001
- ISO 22000
- ISO 31000
- POPIA
- PAIA
- King V
How to choose GRC software.
GRC software solutions vary widely in scope and depth. Use these questions to compare them on what matters once the system is live, not only in the demo.
-
One data model, not a bundle
Ask whether risks, controls, obligations, audits and actions share one data model, or are separate modules sold together. Integrated GRC software links them without reconciliation.
-
Your frameworks and laws
Check coverage of the standards and regulations you answer to, for example ISO 27001, ISO 9001, ISO 14001, ISO 45001 and ISO 31000, GDPR, and in South Africa POPIA, PAIA and King V.
-
Start small, then expand
You should be able to go live with one discipline and add others module by module, rather than commit to a single big-bang rollout.
-
Board-ready reporting
Dashboards and board packs should draw on current data, with an audit trail behind every figure, instead of being assembled by hand each quarter.
-
Adoption by real users
Look for single sign-on, mobile capture for field teams and the languages your people work in. XGRC® supports Microsoft Entra ID sign-on and runs in English, Portuguese, French and Spanish.
-
Integration with what you run
The platform should sit alongside your HR, ERP and IT systems rather than replace them, with API-based integration for data exchange where required.
-
Independent security assurance
Ask for current certification and the hosting region. XGRC® is certified to ISO/IEC 27001:2022 and hosted in Microsoft Azure West Europe (Netherlands).
Integrated GRC software compared with spreadsheets and point solutions.
Most organisations reach integrated GRC software from one of two starting points: spreadsheets, or a growing set of single-purpose tools. Here is how the three approaches compare.
What is GRC software? → GRC vs risk management software → ERM vs GRC →
Outcomes, not just software.
How organisations across manufacturing, mining, logistics, and facilities management use XGRC® in practice.
Vican Manufacturing
A South African paint producer became an industry benchmark for safety, quality, and regulatory compliance through SHEQX® and ISO 9001 implementation.
Download case study →Sandton Plant Hire
Replaced disconnected spreadsheets with SHEQX®, delivering faster SHEQ response times, accurate reporting, and the ability to scale operations without increasing risk exposure.
Download case study →Commercial Cold Holdings
One of the 25 largest refrigerated warehousing providers globally digitised SHEQ workflows to strengthen food safety, product integrity, and compliance with international export protocols.
Download case study →Interwaste
Unified SHEQ processes across multiple regions, significantly reducing reporting effort, accelerating safety action closure, and increasing near-miss reporting volumes.
Download case study →Pple Group
Elevated operational standards across the group through ISO 9001 and SHEQX®, improving quality management and compliance visibility.
Download case study →TN Ceramics
A specialist ceramics supplier to major Southern African mining companies adopted XGRC® to strengthen governance, compliance, and operational oversight.
Download case study →Servest
Digitised SHEQ processes since 2019, reducing administrative burden and achieving renewed ISO 9001, 14001, and 45001 certifications in October 2024.
Download case study →Specific reasons to choose XGRC®.
The XGRC® platform is certified to ISO/IEC 27001:2022, customer data is hosted in Microsoft Azure West Europe (Netherlands), and organisations such as KAP Ltd, African Rainbow Minerals, RCL Foods, Servest, Interwaste and Toyota South Africa rely on it. See our customers or review our security and hosting.
Organisations across Africa, Europe, Australia and the Americas trust XGRC® to drive compliance at enterprise scale, a global platform, wherever they operate.
The XGRC® platform is certified to the latest international standard for information security management.
One auditable data layer across governance, risk, compliance, ESG, and data protection, no double-entry, no tool sprawl.
Purpose-built for South African and UK regulatory environments, POPIA, PAIA, King V, and GDPR, in a single platform.
Common questions about the platform.
What is GRC software?
GRC software brings governance, risk management and compliance activities onto one platform, so policies, risks, controls, audits and obligations are tracked in one auditable place instead of spreadsheets and email. XGRC® adds ESG and data protection (GDPR/POPIA) on the same foundation.
What is the purpose of a GRC tool?
A GRC tool gives leadership one auditable view of governance, risk and compliance. It holds the risk register, controls, policies, obligations, audits and actions together, assigns owners and tracks every action to closure, so evidence is ready when auditors, regulators or the board ask for it.
What are GRC software solutions?
GRC software solutions are the applications that run governance, risk and compliance work: risk registers, policy and obligation management, internal audit, incident and corrective action tracking, and board reporting. They are sold either as separate point solutions or as one integrated GRC platform. XGRC® provides them as specialist solutions on one shared data foundation.
What is a GRC platform?
A GRC platform is GRC software built on one data foundation that several disciplines share, so risk, compliance, audit, ESG and data protection teams work from the same records. Unlike a collection of separate tools, a control, the risk it treats, the obligation it satisfies and the audit that tested it stay linked automatically.
What is integrated GRC software?
Integrated GRC software manages governance, risk and compliance on one connected system rather than in separate tools. A compliance failure updates the risk picture, an audit finding raises a tracked corrective action, and the board sees one current view. XGRC® is built this way, with Enterprise Risk Management, Integrated Assurance, SHEQX®, MSXCyber®, ESG and other solutions sharing one auditable data layer.
How do I choose GRC software?
Start with the frameworks and regulations you must meet. Then check whether the platform holds risks, controls, obligations, audits and actions on one data model, whether you can go live with one discipline and expand, how board reporting is produced, how it handles sign-on, mobile use and languages, how it integrates with your existing systems, and what independent security certification it holds.
What is the difference between GRC software and ERM software?
ERM software focuses on enterprise risk: the risk register, risk appetite, key risk indicators, treatment and board reporting. GRC software is broader and covers governance and compliance as well as risk. In XGRC®, Enterprise Risk Management is the risk pillar of the GRC platform, so you can start with ERM and connect compliance and assurance later.
Is GRC software only for large enterprises?
No. XGRC® customers range from a single regional operation to the multinational headquarters it reports into. Smaller organisations usually start with one discipline and add more as their obligations grow.
How is XGRC® different from point solutions?
Most organisations run separate tools for risk, audit, ESG and compliance, each with its own data model. XGRC® connects them on one data layer, so a risk links to its controls, its audit findings, and its remediation actions automatically, no duplicate entry, no reconciliation between systems.
Does XGRC® support POPIA and GDPR?
Yes. XGRC® is purpose-built for South African and UK/EU regulatory environments, with dedicated workflows for POPIA, PAIA, King V and GDPR data protection obligations, including data subject access requests and privacy impact assessments.
How long does implementation take?
Implementation scope depends on how many disciplines (risk, audit, ESG, compliance, safety) and business units you bring onto the platform at once. Most customers start with one discipline live within weeks, then expand module by module rather than a single big-bang rollout.
Is XGRC® secure and independently certified?
Yes. The XGRC® platform is certified to ISO/IEC 27001:2022 for information security management, and customer data is hosted in Azure West Europe (Netherlands).
Does XGRC® support single sign-on?
Yes. Users can sign in to the XGRC® platform with their Microsoft work accounts through single sign-on with Microsoft Entra ID (Azure Active Directory), so they use the same sign-in they already have.
Which languages is XGRC® available in?
The XGRC® platform is multilingual. It is available in English, Portuguese, French and Spanish, and can be translated into further languages on request.
Can XGRC® be used on mobile devices?
Yes. SHEQX® has native iOS and Android apps for field work, including offline capture on sites with no signal that syncs when the device reconnects. The rest of the platform runs in any modern browser.
Can XGRC® integrate with our existing systems?
Yes. XGRC® is designed to sit alongside your existing HR, ERP and IT systems rather than replace them, with API-based integration available for data exchange where required.
Take control of governance, risk, compliance and data protection.
Whether you are addressing a single risk domain or coordinating assurance across the enterprise, XGRC® gives you the foundation to move forward with confidence.
[email protected] · +27 (0)87 802 0179