Enterprise Risk Intelligence
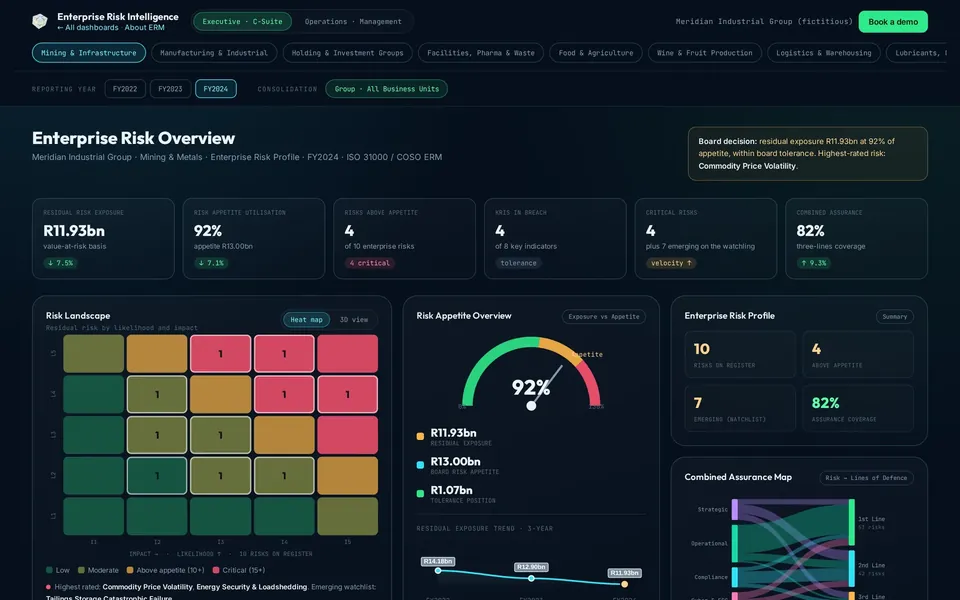
Board-level risk appetite, a 5x5 heat map, KRIs and combined assurance, across nine industries and three reporting years.
- Risk appetite
- Heat map
- Combined assurance
17 interactive dashboards built on the XGRC® platform. Filter them, drill into any KPI to see how it is calculated, switch industries, and export a board pack. No sign-up needed.
Every company, person and figure in these dashboards is fictitious and illustrative. Nothing is connected to a live system or to any customer.
Board-level risk appetite, a 5x5 heat map, KRIs and combined assurance, across nine industries and three reporting years.
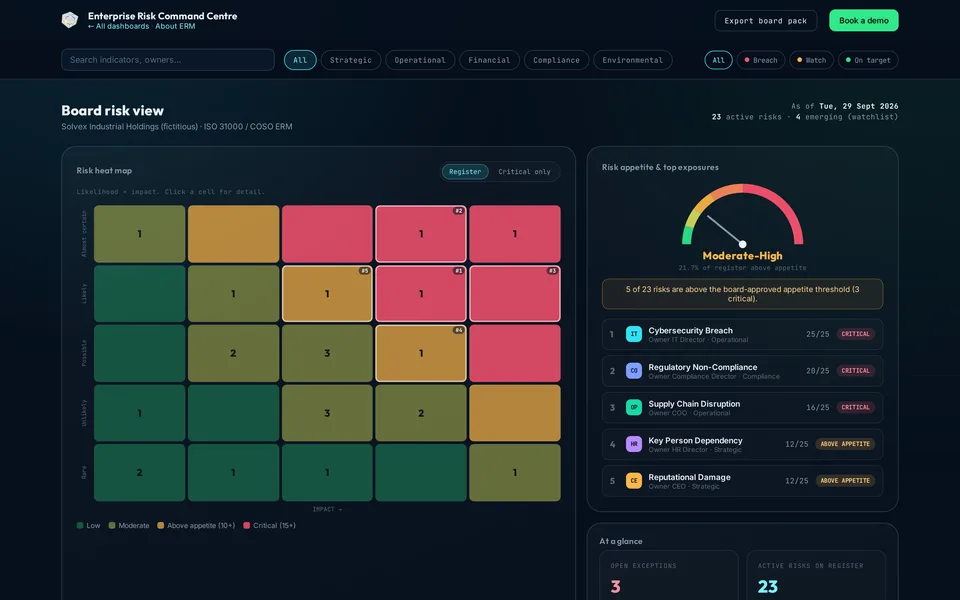
A single-company command centre: heat map, risk appetite gauge, key risk indicators and category trends, reconciled to one register.
Safety, health, environment, risk and quality in one view, from LTIFR and permits to certification status, site by site.
EU AI Act classification, ISO/IEC 42001 controls and evidence, with XLOGIC®, Asgard and MAIA® signals correlated per AI system.
Volume, severity and closure speed across sites, the near-miss ratio as a leading indicator, and root causes ranked by impact.
Supplier tiering, due-diligence currency, spend concentration and contract renewals, with the vendors that need attention first.
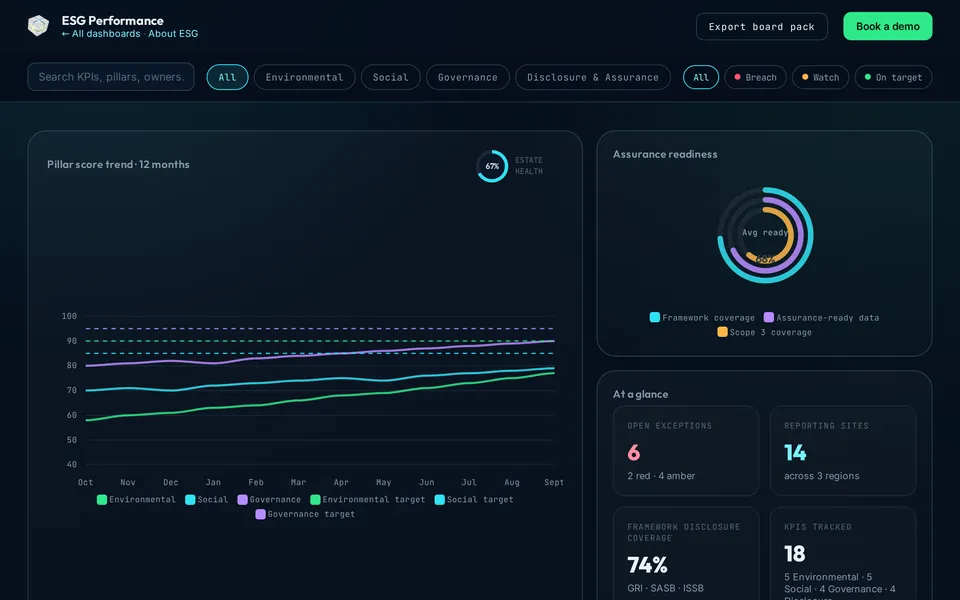
Environmental, social and governance KPIs against targets, a materiality matrix and disclosure readiness for GRI and ISSB.
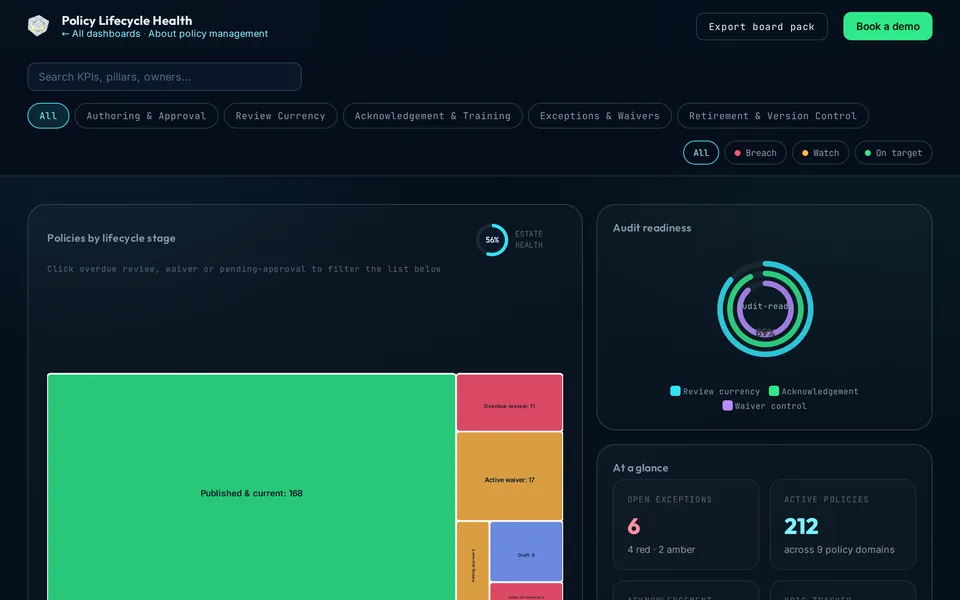
Review currency, acknowledgement by department, waivers and upcoming reviews for the whole policy estate.
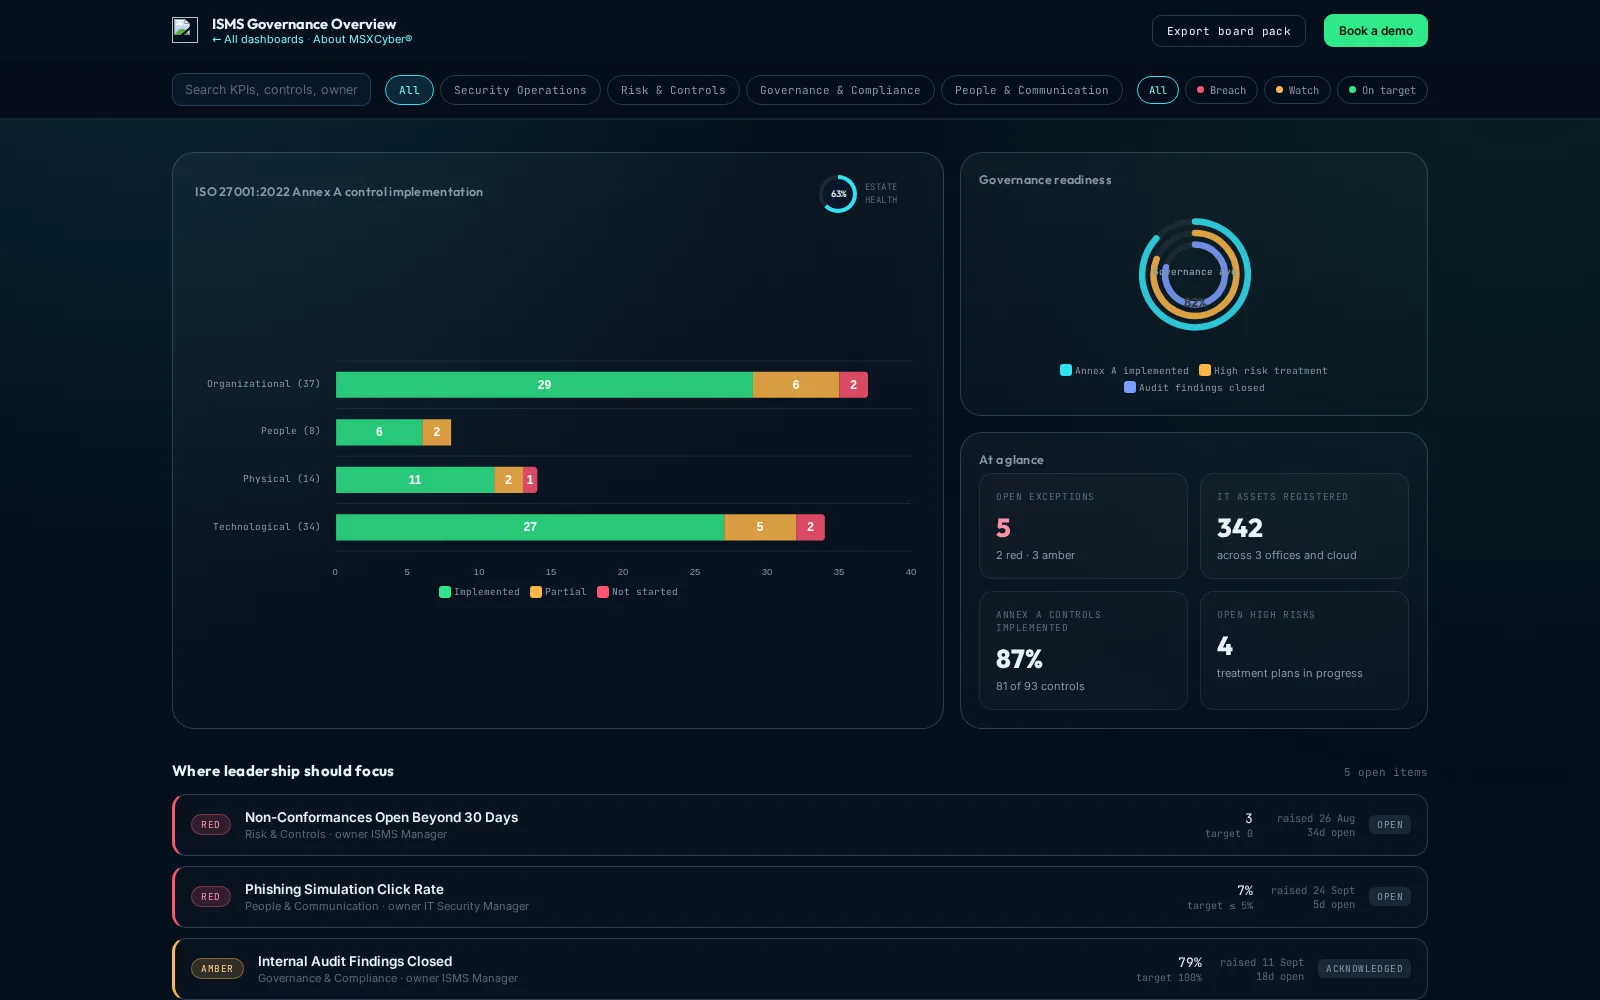
ISO 27001:2022 Annex A control implementation, risk treatment and internal audit findings, reconciled in one ISMS dashboard.
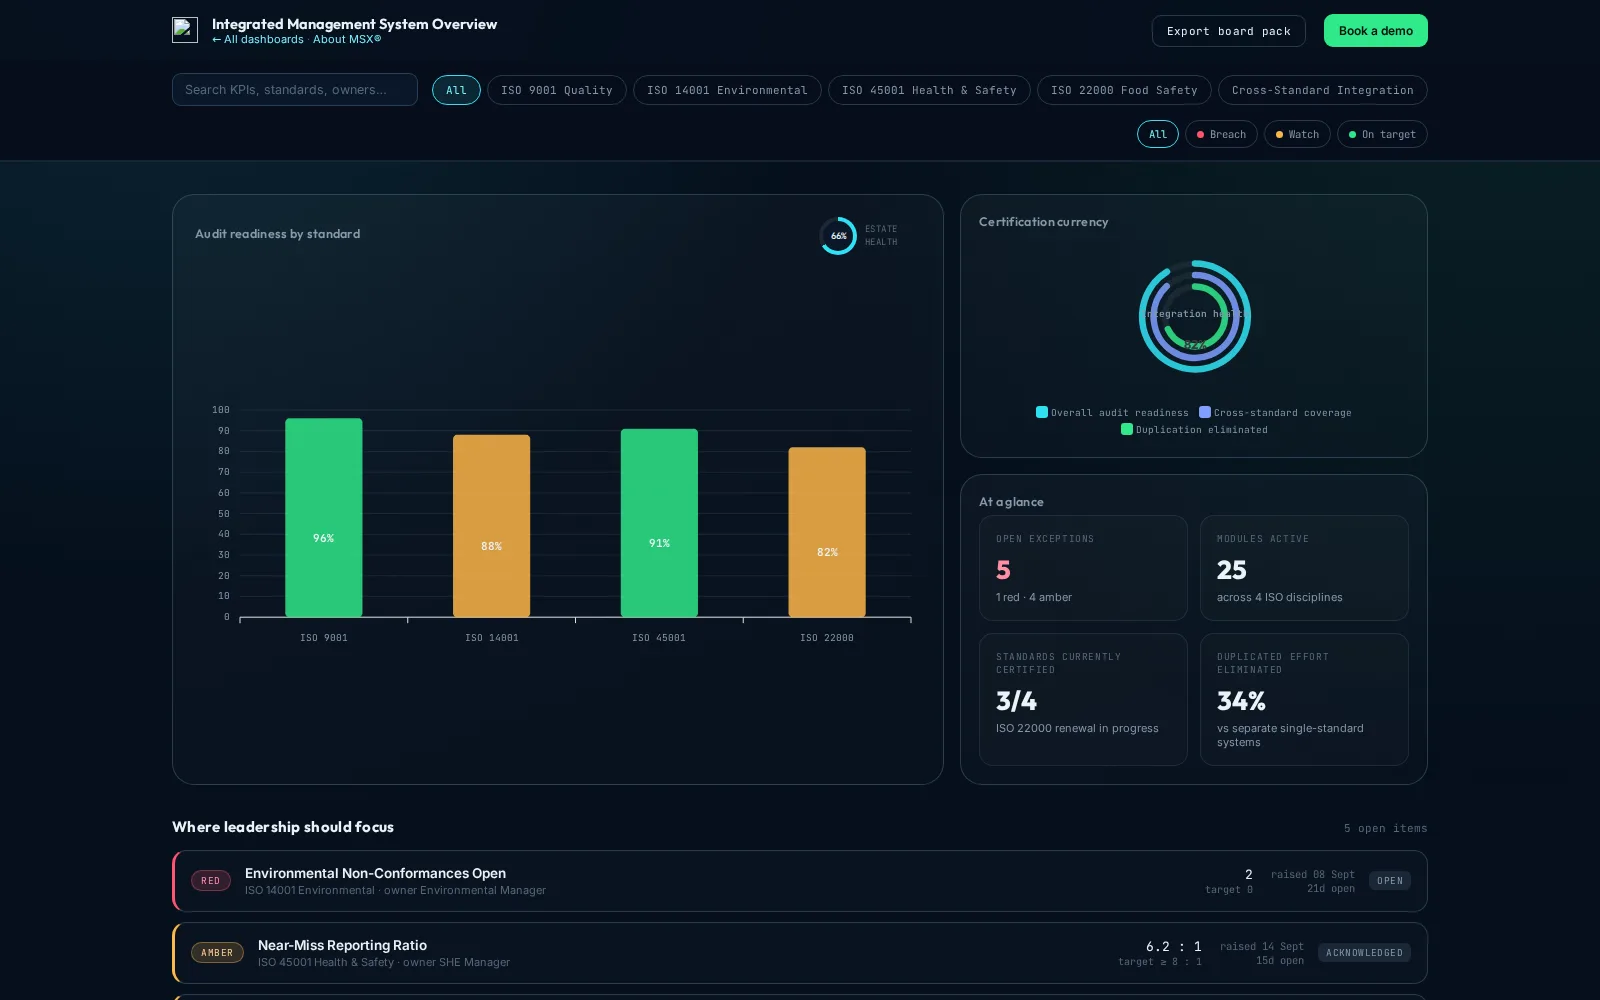
Audit readiness and certification currency across ISO 9001, 14001, 45001 and 22000, on one integrated management system.
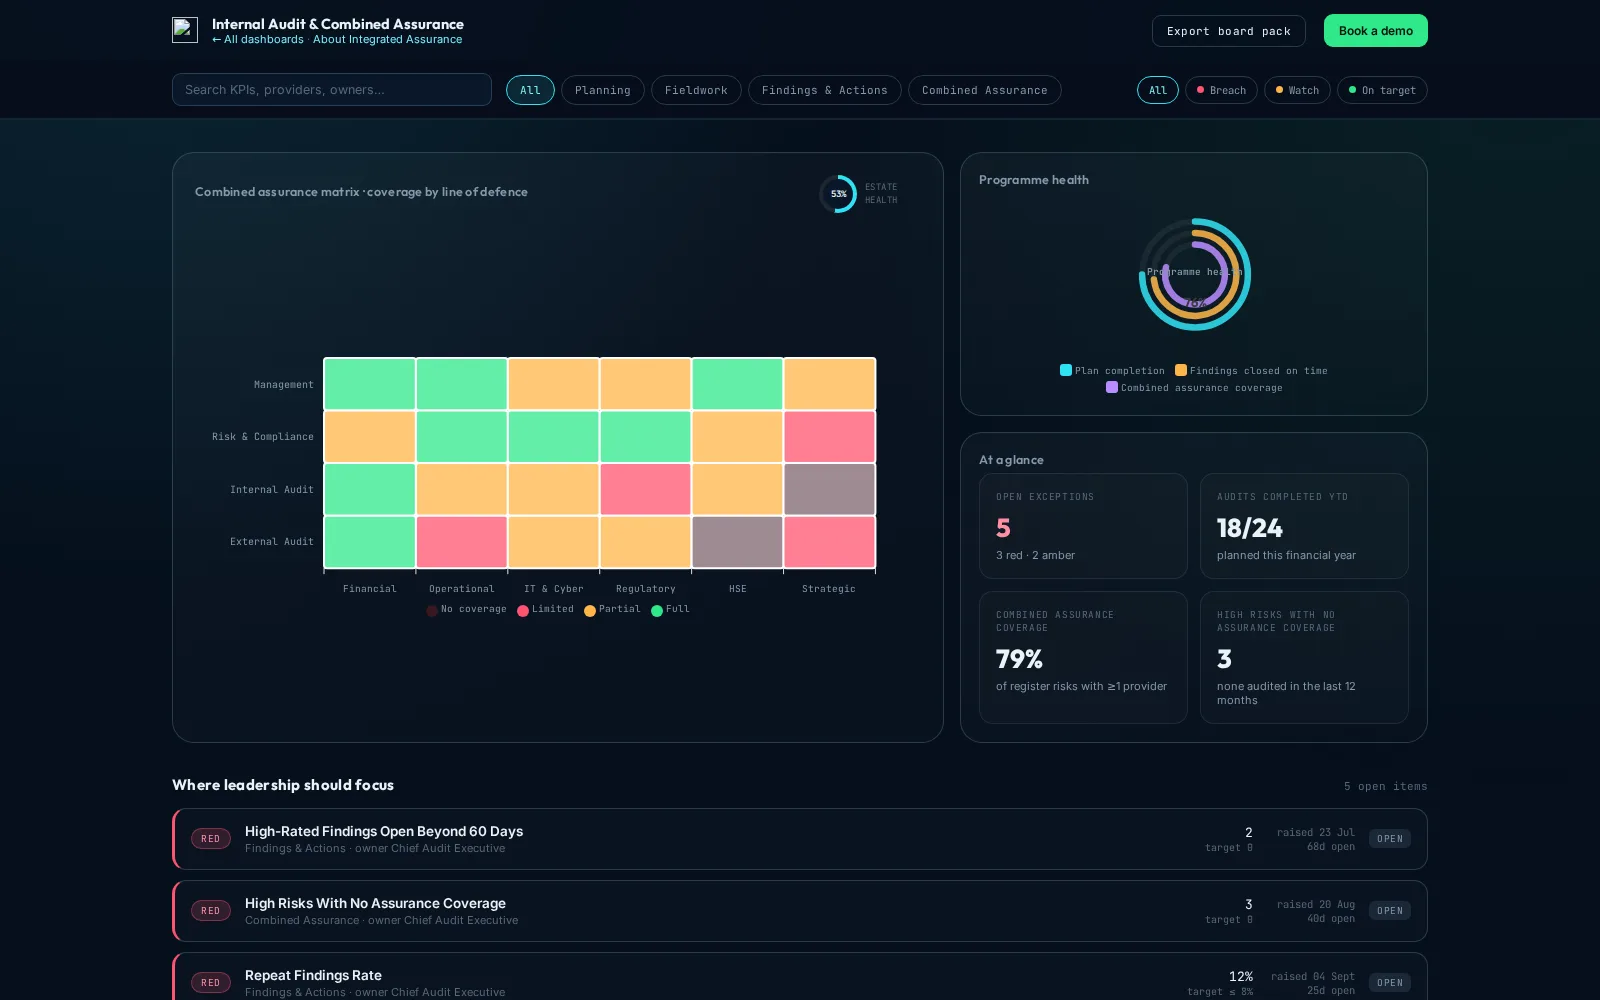
Risk-based audit planning, findings ageing and the combined assurance matrix across all four lines of defence.
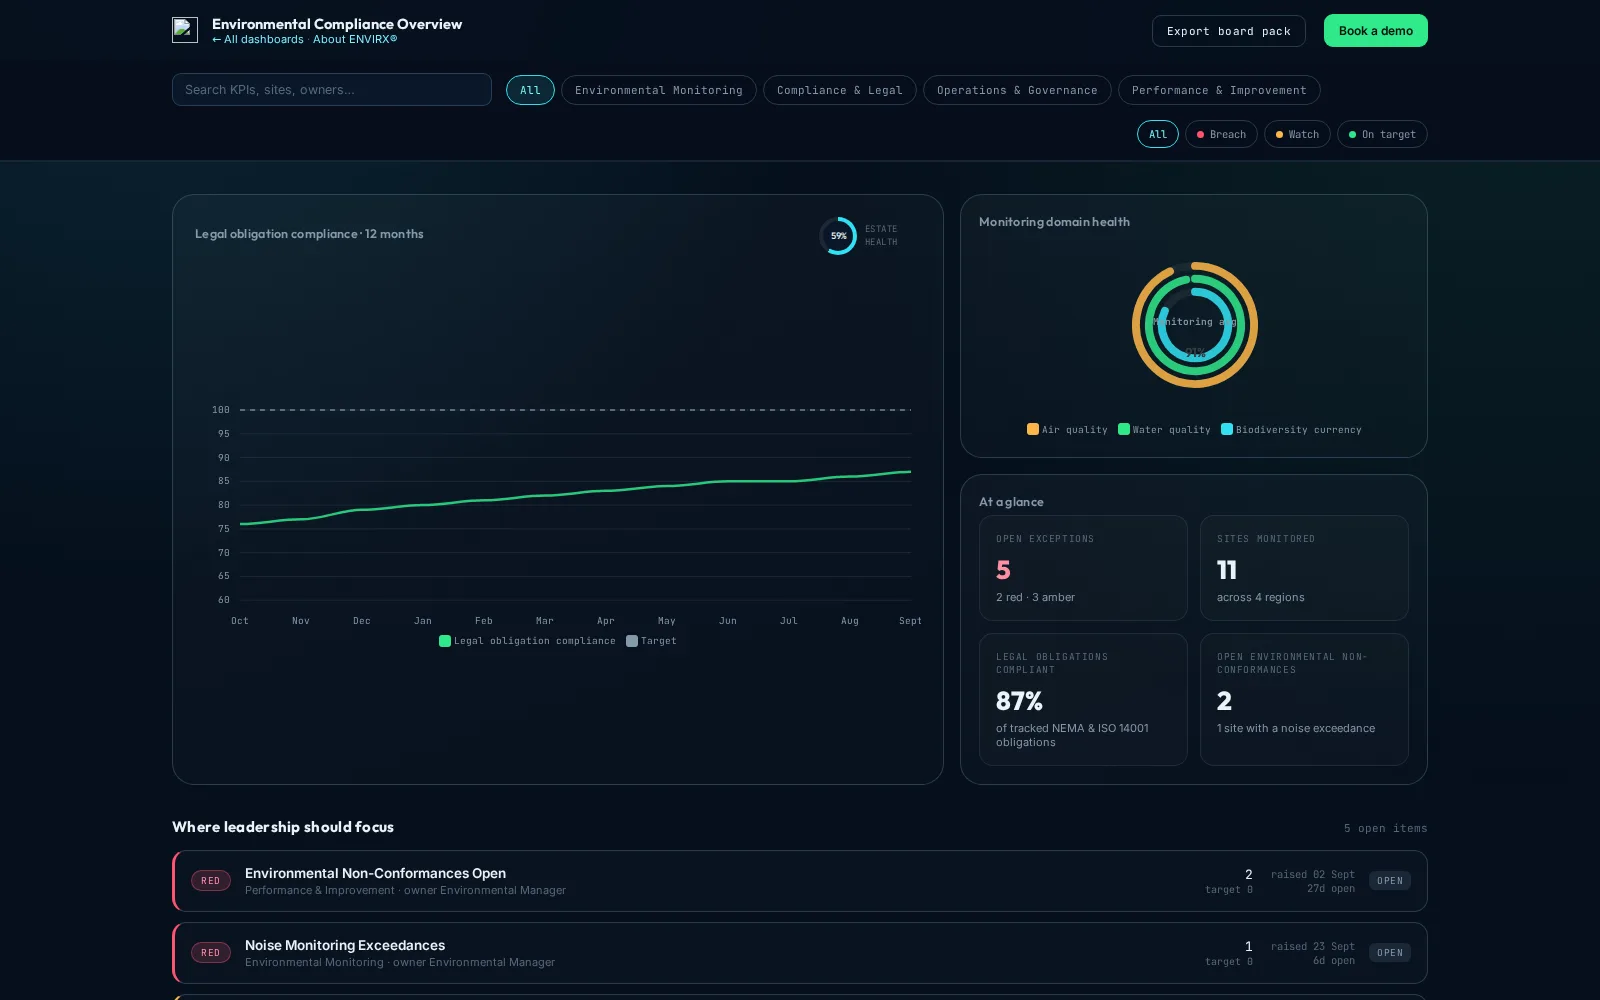
Legal obligation compliance, multi-site environmental monitoring and non-conformances, aligned to ISO 14001.
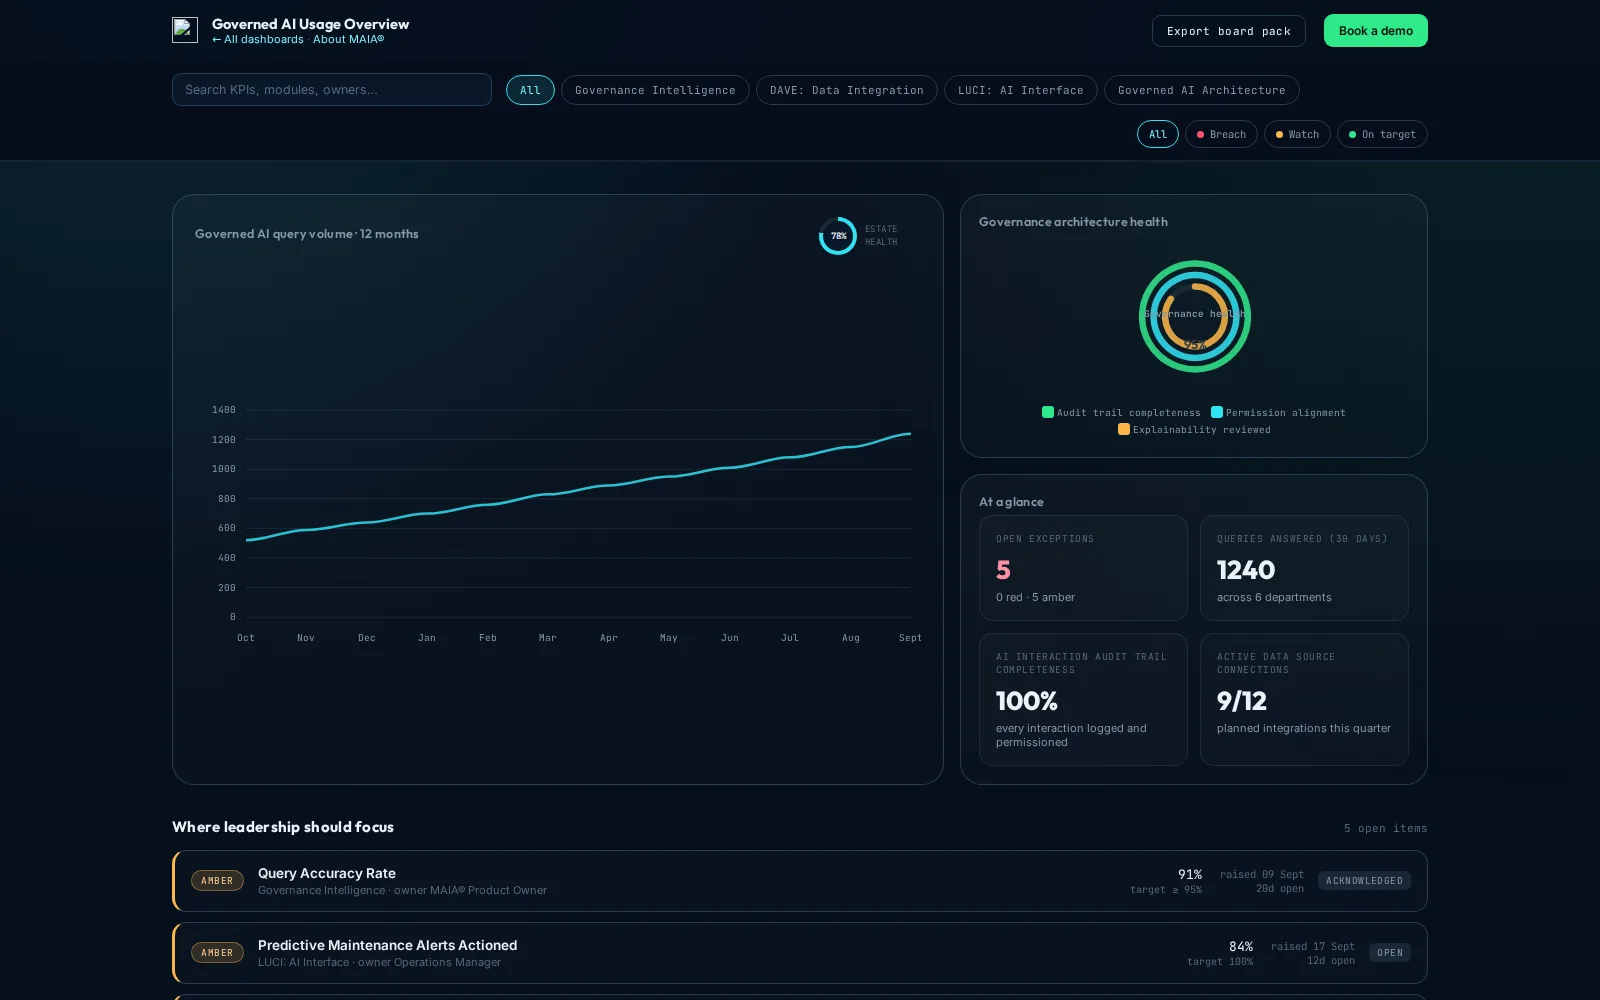
Query volume, department adoption and a complete AI interaction audit trail for governed AI across XGRC®.
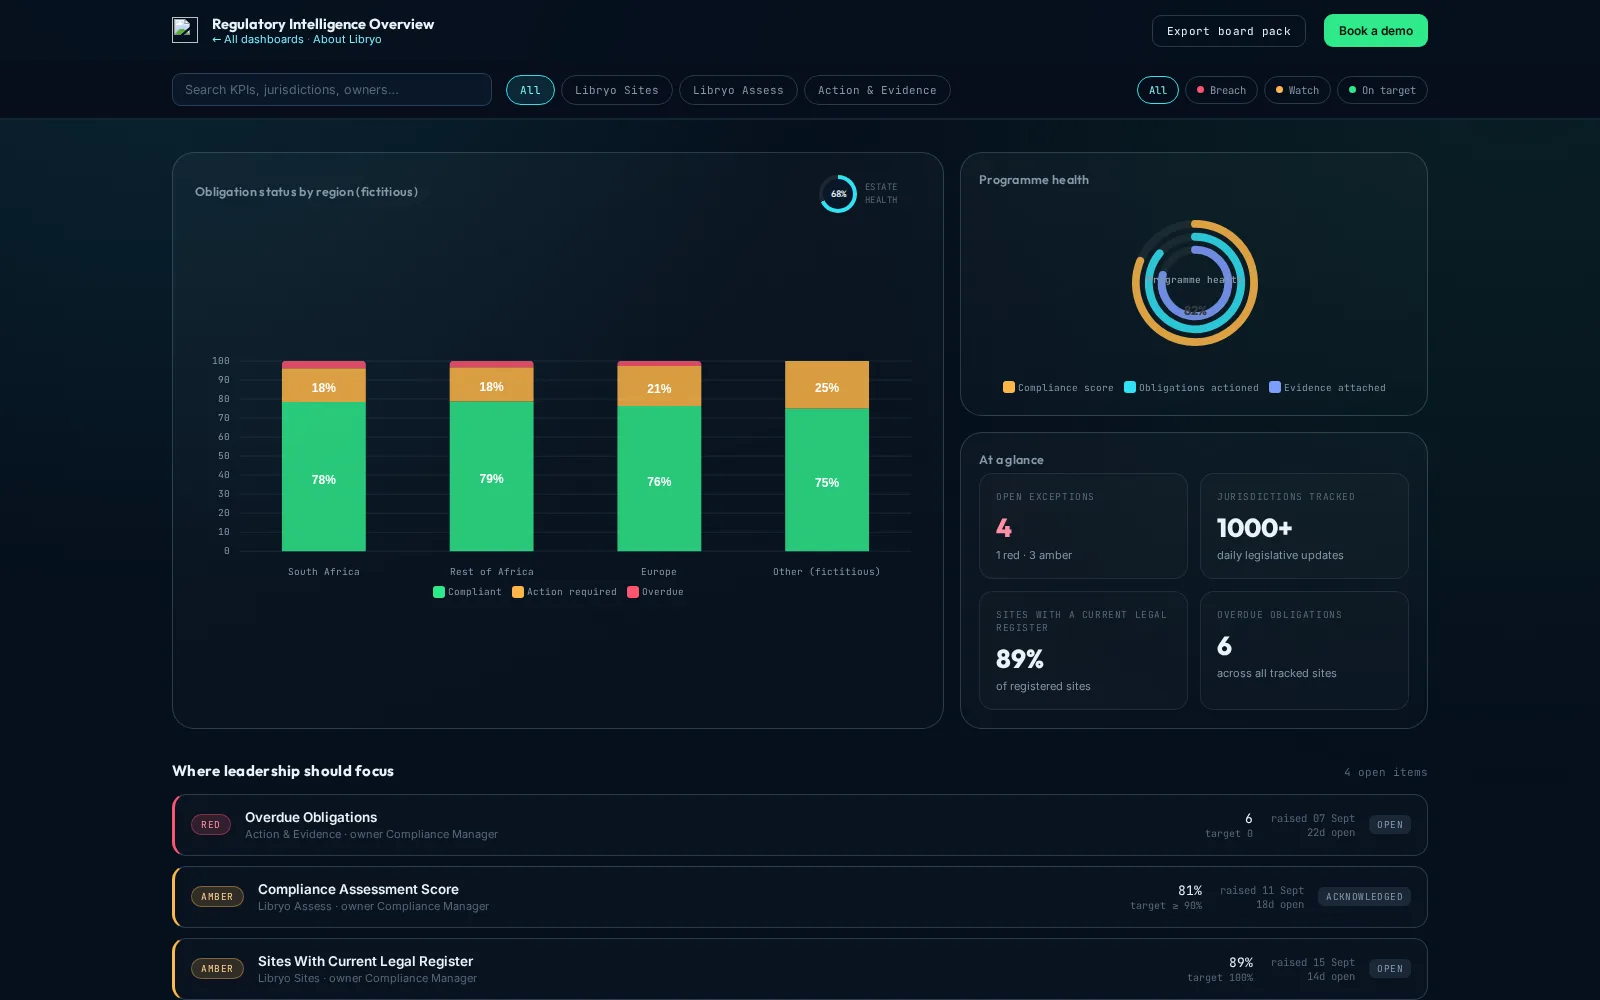
Multi-jurisdiction obligation status, compliance scoring and evidence-backed closure, powered by Libryo inside XGRC®.
AI-driven penetration testing, unified vulnerability visibility and dark web monitoring, feeding governed risks into MSXCyber®.
Weighted pipeline, win rate, forecast accuracy and approval governance, with a full audit trail on every deal.
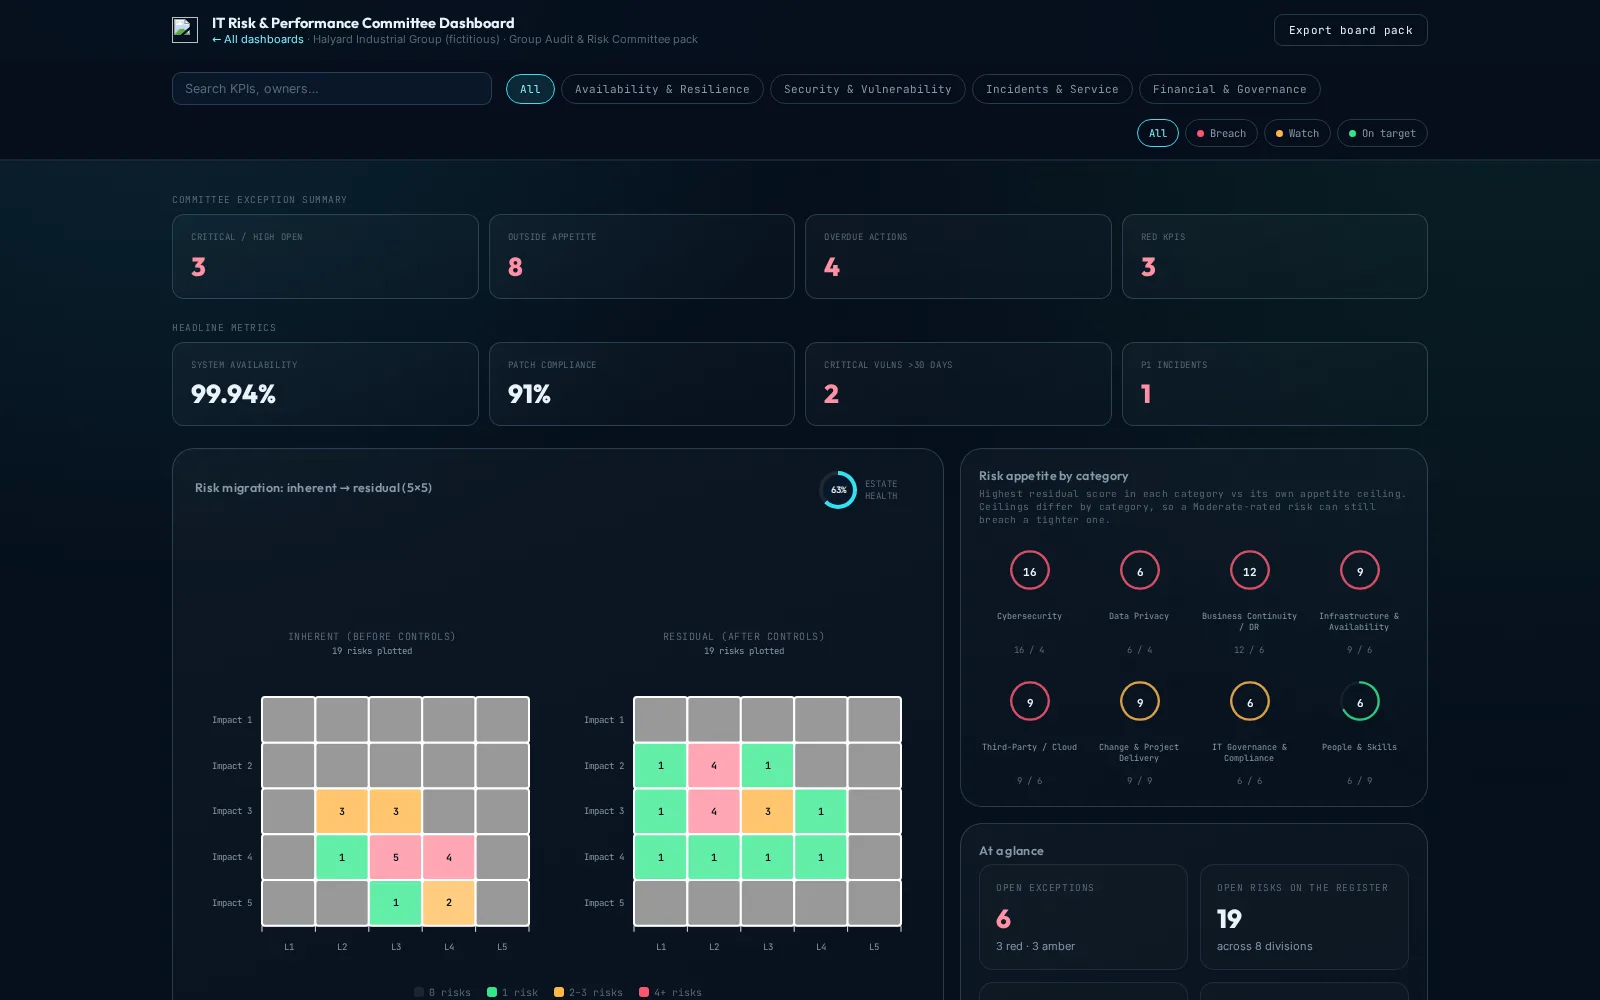
A group IT risk register and KPI scorecard for the audit committee, with category-specific risk appetite and an inherent-to-residual risk migration view.
Use the tabs, the breach and watch filters or the search box to narrow any dashboard to one pillar, owner or status.
Every tile opens its definition, owner, refresh cadence and the exact calculation behind the number.
Generate the PDF a board would receive, with every open exception, its owner and how long it has been open.
A 30-minute walkthrough with an XGRC® specialist, on your registers, your sites and your frameworks.
Cookies on xgrcsoftware.com
We use analytics and advertising cookies to understand how the site is used and to measure our campaigns. They are only set if you accept. Read our Cookie Policy.