MSXCyber® ISMS and IT risk management software
ISO 27001 compliance without the spreadsheet chaos.
MSXCyber® is IT risk management software and a complete Information Security Management System (ISMS) aligned to ISO 27001:2022, with governance, risk management, and audit-ready evidence built in from day one. Data breaches now carry material financial, regulatory and operational consequences. Structured ISMS governance is no longer optional.
Download: Infographic (PDF)
What is MSXCyber®?
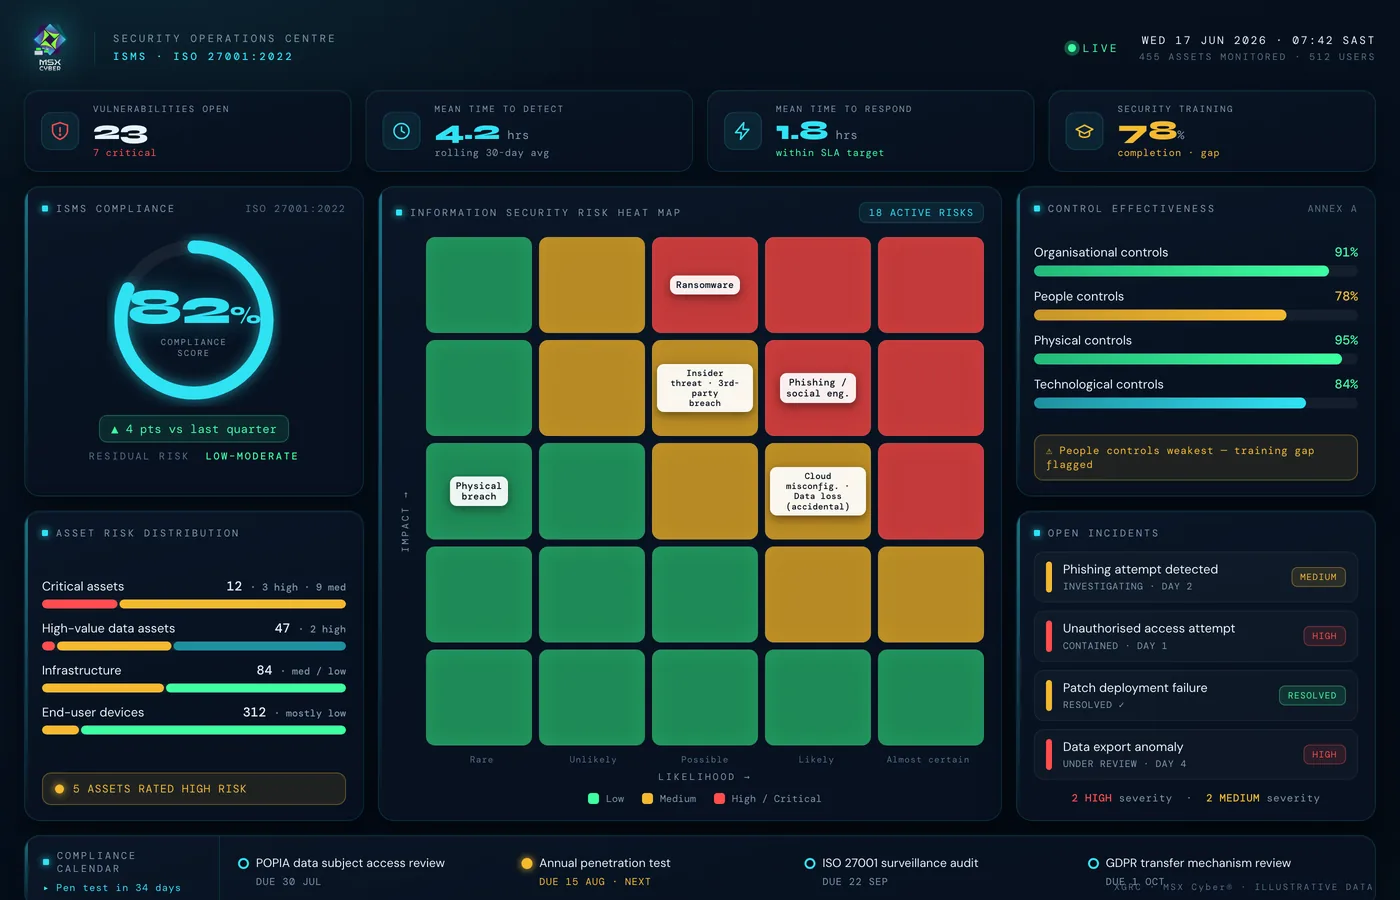
ISMS software helps organisations manage information security governance, risk assessment, controls, incidents, internal audits and evidence required to support an ISO 27001-aligned Information Security Management System.
Organisations typically adopt MSXCyber® when ISO 27001 evidence, asset inventories and incident response plans are still managed through spreadsheets and email, and they need continuous, audit-ready ISMS governance rather than a scramble before each certification review.
What breaks without MSXCyber®.
ISO 27001 gaps only found at audit
Without continuous monitoring, control weaknesses accumulate quietly between certification reviews.
Asset inventories in spreadsheets
Assets undocumented, risks unassessed. One security incident reveals just how fragile the inventory actually is.
No structured incident response
When a breach occurs, the response is improvised. Regulatory disclosure obligations are missed. Costs escalate.
GDPR and POPIA obligations untracked
Data protection compliance managed through email threads, no evidence trail, no audit readiness.
How MSXCyber® works.
MSXCyber® implements the full plan-do-check-act cycle for information security, from asset registration and risk assessment through control implementation, incident management, internal audit, and management review, on a single governed platform.
See it in action →MSXCyber® in practice.
See MSXCyber® running.
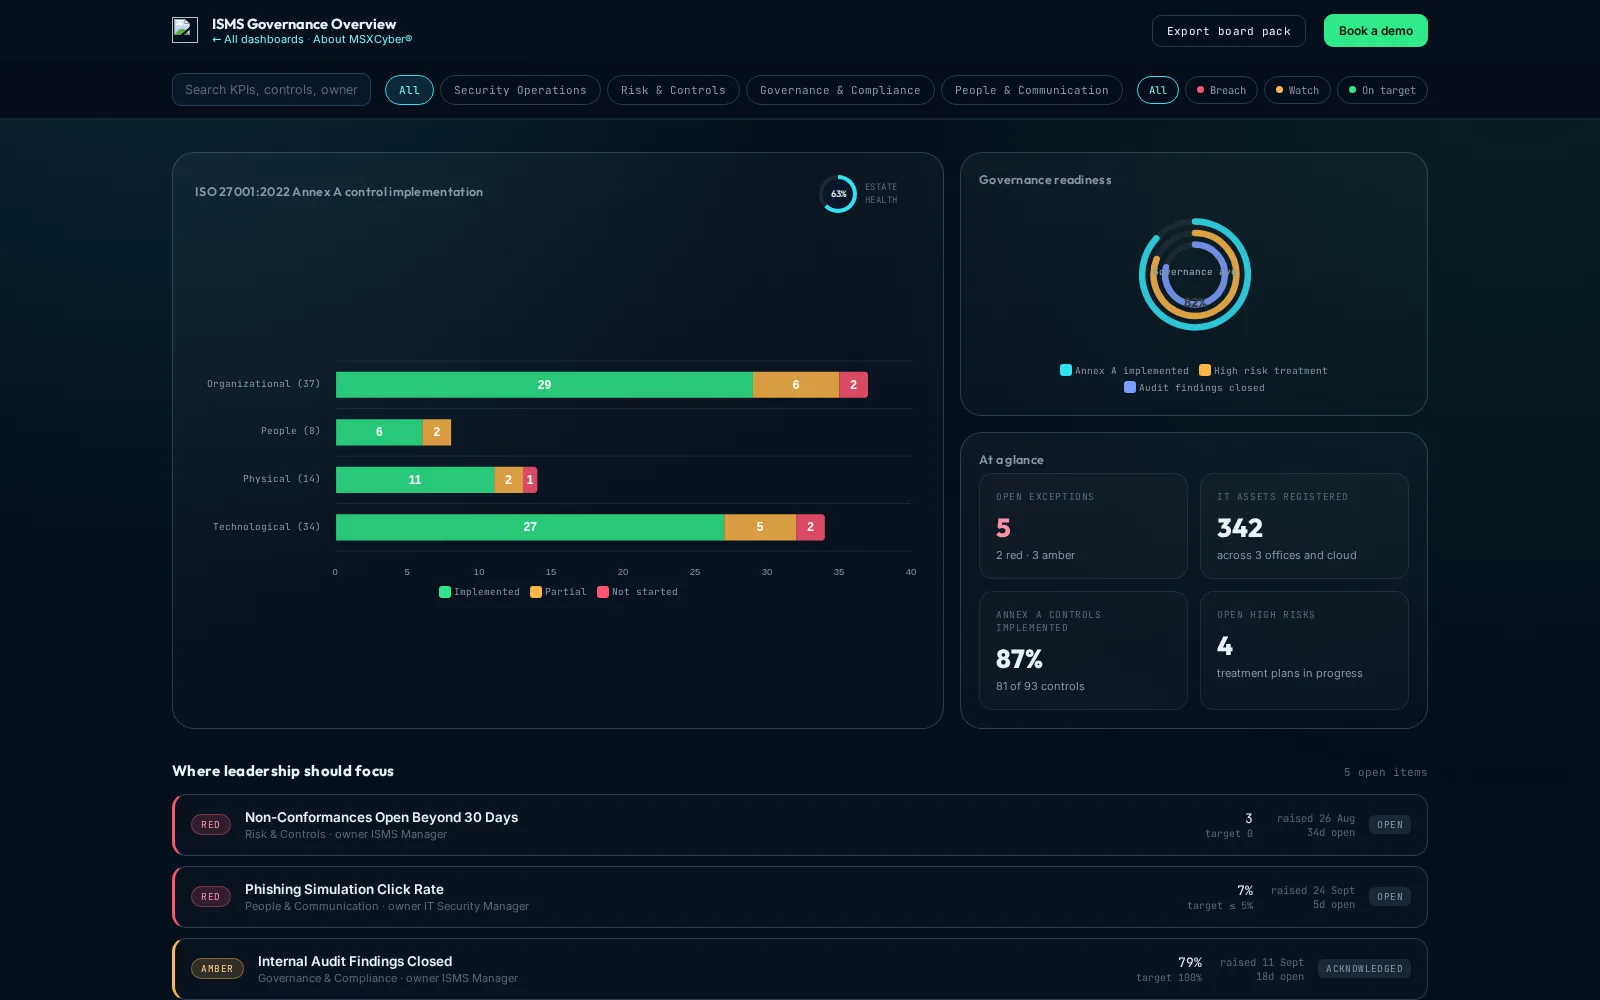
An interactive demonstration dashboard with fictitious data. Filter it, open any KPI to see how it is calculated, and export a board pack.
Everything in MSXCyber®.
Core capabilities are configured to your requirements, with the flexibility to expand as your needs grow.
Security Operations
Risk & Controls
Governance & Compliance
People & Communication
What IT risk management software does.
IT risk management software gives an organisation one governed place to identify, assess, treat and monitor risks to its information, systems and services, and to prove to auditors and the board that the controls behind those risks are working. MSXCyber® does this inside an ISO 27001:2022 aligned ISMS, so IT, cyber and information security risk are managed in the same plan-do-check-act cycle as the rest of the management system.
Know what you are protecting
An asset register records information assets, systems and owners, so every IT risk is tied to something real and someone accountable.
Assess IT and cyber risk
Risk assessments score likelihood and impact for information security and cyber threats, and record the treatment chosen for each risk.
Run and evidence controls
Controls, change management and non-conformances are tracked with owners and due dates, so the evidence for each control builds up as work is done.
Handle incidents and events
Event management and monitoring capture security incidents and link them back to the risks and controls they affect.
Audit and review
Internal audits, document control and management review run on the same platform, ready for ISO 27001 certification and surveillance audits.
Meet privacy obligations
GDPR, POPIA and NIS Directive requirements sit alongside ISO 27001, so data protection and information security share one framework.
Streamlining ISO 27001 compliance →ISO 27001 readiness checklist →
How IT risk connects to enterprise risk.
IT and cyber risks rarely stay inside the IT department: an outage or breach becomes an operational, financial and reputational risk. Because MSXCyber® runs on the same XGRC® platform as Enterprise Risk Management, significant IT risks can be escalated into the enterprise risk register and reported to the board, without copying data between systems.
MSXCyber® governs the processes around your technical security tools; it does not replace firewalls, endpoint protection, vulnerability scanners or SIEM platforms. For penetration testing and vulnerability visibility, findings from the partner solution Hakware feed into MSXCyber® as governed risks and actions.
Enterprise risk management software →Hakware penetration testing →
What teams use MSXCyber® for.
Each use case explains the problem, the standards and regulations involved, and how MSXCyber® handles it in practice.
GDPR Compliance
XGRC® gives data protection teams a structured way to manage GDPR obligations — lawful basis and consent, data subject requests, DPIAs, and breach notification — on one auditable platform, with every processing activity linked to its evidence.
View use case → RegulatoryPOPIA Compliance
XGRC® gives Information Officers a structured way to manage POPIA obligations on one auditable platform, including processing conditions, data subject rights, and security compromise reporting to the Information Regulator.
View use case → ISO ReadinessISO 27001 Readiness
XGRC® MSXCyber® gives organisations a structured way to assess ISO 27001 readiness, close control gaps, and manage the information security management system all year round, not just in the weeks before an audit.
View use case → ISO ReadinessISO 27001 Documentation Checklist
What ISO/IEC 27001:2022 actually requires, what auditors expect to see, and what is worth adding once the basics are solid. Sorted into four tiers, with the clause or Annex A control for every item.
View use case →MSXCyber® is stronger on the platform.
Every XGRC® solution shares the same data foundation. When MSXCyber® is combined with other solutions, risk, compliance, assurance, and governance data flows without duplication.
What MSXCyber® is not.
MSXCyber® supports information security governance and ISO 27001-aligned management processes. It does not replace technical security tools such as firewalls, endpoint protection, vulnerability scanners or SIEM platforms, for offensive security testing and vulnerability scanning, XGRC® partners with Hakware.
Common questions.
What is IT risk management software?
IT risk management software is a system for identifying, assessing, treating and monitoring risks to an organisation's information, systems and services, with owners, controls and evidence recorded in one place. MSXCyber® provides this within an ISO 27001:2022 aligned ISMS.
What is the difference between IT risk management software and ERM software?
IT risk management software focuses on information, systems and cyber threats, usually within an ISMS. Enterprise risk management software covers every category of risk across the organisation. On XGRC®, MSXCyber® and ERM share one platform, so significant IT risks can be escalated to the enterprise risk register.
Is MSXCyber® cyber risk management software?
Yes. MSXCyber® manages cyber and information security risk assessments, controls, incidents and audits. It governs the processes around technical security tools rather than replacing them.
Does MSXCyber® replace our firewall or antivirus software?
No. MSXCyber® governs your ISMS, risk, controls, incidents and audit evidence. It does not replace technical security tools; it governs the processes around them.
Is MSXCyber® aligned to ISO 27001:2022?
Yes. MSXCyber® implements the full plan-do-check-act cycle aligned to ISO 27001:2022, alongside GDPR, POPIA and NIS Directive requirements.
Can MSXCyber® help with GDPR and POPIA compliance?
Yes. MSXCyber® links data protection obligations, processing records and incident response to the same ISMS governance framework.
How does MSXCyber® relate to Hakware?
MSXCyber® governs your ISMS; Hakware is a partner solution that provides AI-powered penetration testing and vulnerability visibility. Findings from Hakware feed directly into MSXCyber® as governed risks and actions.
See MSXCyber® running in your environment.
Talk to an XGRC® specialist about how MSXCyber® fits your organisation's specific compliance and governance requirements.
[email protected] · +27 (0)87 802 0179