A board is considering a new market, a major supplier or an AI-enabled service. The financial case is prepared and the delivery plan looks achievable. Only then is the compliance team asked to review a decision that is nearly complete.
There is a better point to contribute: while the options are still being designed. At that stage compliance can show which requirements affect each option, what must change before the business can proceed, which controls already provide a foundation, and where the evidence is too weak to support confidence. The future of compliance should be judged by that contribution. Not by how many reports the function produces, but by whether its knowledge improves the choices the organisation makes.
From Reporting Activity to Informing Strategy
COSO's enterprise risk management framework explicitly connects risk with strategy-setting and performance. ISO 37301 provides a management-system approach for evaluating and improving compliance. Neither idea requires compliance to operate as a separate year-end reporting exercise, and the relationship between the two disciplines is explored further in ERM versus GRC.
Bring compliance knowledge into planning. A requirement may affect a launch date, delivery model, supplier choice or resource allocation, so make those constraints visible while the design can still change. Commercial attractiveness does not make an unmet mandatory requirement acceptable. Where the position is unclear, obtain specialist interpretation before treating an internal approval as authority to proceed.
What Makes Compliance Information a Strategic Asset
A document is not strategically valuable merely because it is stored centrally. Its value depends on whether someone can use it to make a better decision. Link a service obligation to its owner, relevant controls, current evidence and unresolved findings, and the record can then help answer a practical question: are we ready to expand this service?
Here, a strategic asset means reliable organisational knowledge and the processes that maintain it. It is not an accounting claim. Choose a real decision and ask what information would change it, then build the connections needed to answer that question rather than collecting every field the software allows. The same evidence that supports a decision internally can also support customers' decisions, which is why compliance is becoming a competitive advantage.
Put Compliance Into the Investment Case
Consider an illustrative proposal to launch a managed service across several customer sites. One option launches every site together. Another begins with a limited group while the organisation completes training, supplier checks and control testing for the remaining locations. A third changes the service design to avoid an activity the business is not ready to govern.
A strategic compliance contribution explains the conditions and trade-offs attached to each option. It sets out which requirements apply and which can already be demonstrated, what work remains and who owns it, and where the plan depends on a supplier or an external approval. The board can then compare options using more than projected revenue and implementation cost, considering readiness, delivery constraints and uncertainty as part of the decision itself.
A group-wide compliance percentage cannot show those trade-offs. Leadership needs the conditions attached to the proposed activity.
Connect the Records Without Erasing Their Differences
Connect each obligation to the affected process, risk, controls, owner, evidence and assurance results. Reviewers should be able to trace the decision and understand what has changed.
Do not confuse connection with equivalence. Similar obligations may apply to different entities, populations or periods, and one control might support both but require separate evidence. Preserve the source, applicability and mapping rationale, together with material changes and decisions. Simpler reporting must not erase distinctions that matter.
More Continuous Does Not Mean Everything Must Be Live
Compliance information becomes useful when it is refreshed at the pace of the risk and the decision. That does not mean every control needs second-by-second monitoring. An access change may need immediate review. A supplier assurance record may need reassessment after a material change. A strategic commitment may need attention through scheduled management review. Define the trigger and the responsible person for each, rather than applying one interval to everything.
Also make the age and completeness of evidence visible. A dashboard refreshed this morning can still contain an assessment that no longer reflects the service. A status should distinguish supported confidence from an untested assumption.
AI Can Assist the Work, but It Also Needs Governance
AI creates two separate questions for the compliance function: how might it assist the work, and how should the organisation govern its own AI use?
For the first question, candidate uses include summarising records, grouping similar findings and preparing questions for review. Treat these as assistive tasks to evaluate, not permission for a model to decide that an obligation has been met, and check the source, completeness and suitability of material outputs before relying on them. That is the principle behind governed AI for GRC.
For the second question, the NIST AI Risk Management Framework provides voluntary guidance for incorporating trustworthiness into AI design, use and evaluation, and ISO/IEC 42001:2023 sets requirements for an AI management system. Both support a structured approach rather than adding AI without an operating framework. In practice, keep ownership, approved purpose, risk and impact assessment, controls, changes and evidence connected. A new data source or permission can change an approved use case even when the product name stays the same.
XGRC® AI Governance belongs in that wider programme, applying the connected-governance approach to the decisions, responsibilities and evidence around AI. XGRC®'s AI change management process supports classification, review, approvals, testing and post-launch monitoring. AI-assisted compliance and governance of AI are different activities, and neither removes accountable judgement.
Assurance Must Remain Able to Challenge the Story
The IIA's Three Lines Model distinguishes management's ownership of risk from internal audit's independent assurance. Coordination supports governance, but it must not turn the control owner into the independent assessor of their own work.
Apply that distinction to shared reporting. Show who performed a test, what it covered, the result and any limitation. Where several teams rely on one piece of work, make that reliance visible and assess whether it meets each team's purpose. Do not let a combined dashboard suggest assurance where none exists: an untested critical control should remain visible as an uncertainty, even if every surrounding administrative task is complete.
How XGRC® Supports the Shift
XGRC® Software is GRC software that links governance, risk, compliance and assurance information, including obligations, controls, audits and actions. This supports a connected view of the records needed for oversight and decision-making. XGRC® Enterprise Risk Management, aligned to ISO 31000 and COSO, manages enterprise, operational and project risk on the same auditable platform.
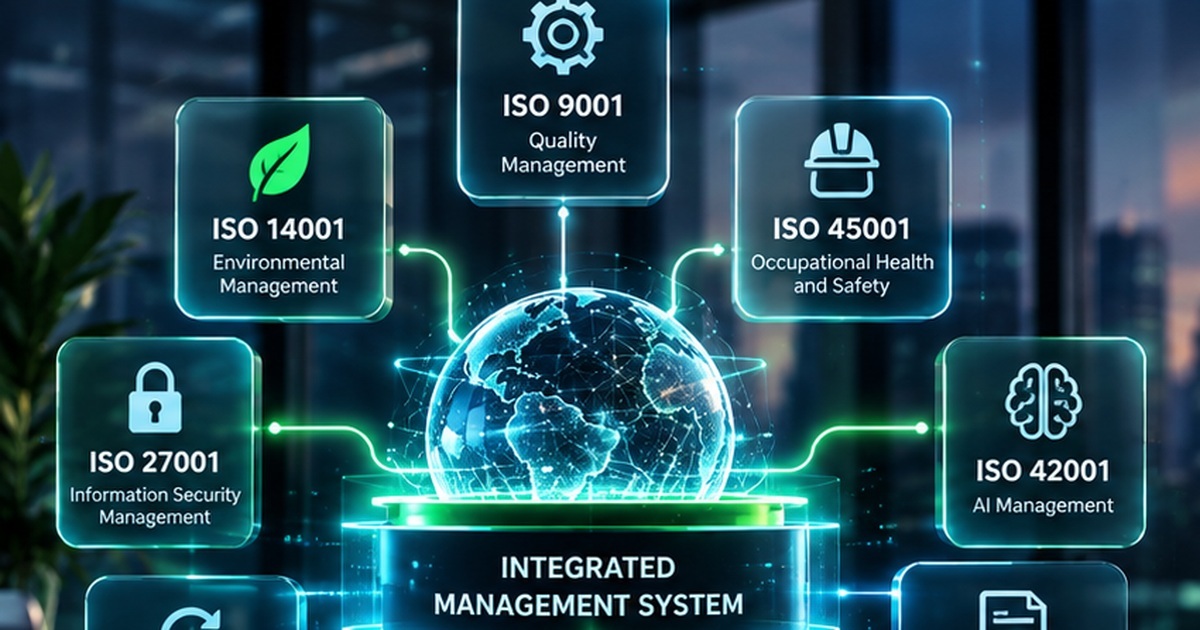
MSX® supports a coordinated management programme with shared document control, governance workflows and performance evaluation. Integrated Assurance connects audit planning, testing, findings and corrective actions with risks and assurance coverage.
Use those capabilities to answer a strategic question. For a proposed expansion, identify the relevant requirements, the controls already tested, the open findings and the work needed before approval. Retain the decision and revisit its conditions when circumstances change. The platform provides structure and visibility. It does not replace a competent assessment, implement every operational control or make a business decision on leadership's behalf.
Start With One Decision, Then Build the Capability
Start with one material decision. The following 90-day approach is a suggested exercise, not a timetable prescribed by a standard.
First, define the decision and its evidence. Choose a launch, contract renewal or operational change. Identify the requirements that influence it, the responsible owners and the information leadership actually needs, rather than the information that is easiest to produce.
Next, connect and challenge the records. Link the relevant controls, assessments and findings to that decision. Test a sample of the evidence, identify gaps and assign the work needed to resolve them to named owners with realistic dates.
Then, use the result in a live review. Present the options, conditions and remaining uncertainty to the people making the decision. Record the decision, its rationale and the events that would trigger reconsideration, so the conditions can be revisited when circumstances change.
Test the approach before expanding it.
Measure Decision Quality, Not Reporting Volume
Useful measures might include material decisions reviewed before commitment, actions completed before a launch condition takes effect, and significant changes that received timely reassessment. Check the quality behind the number. Was the review capable of changing the proposal, or did it simply endorse an existing decision? Did a closed action include credible evidence? Was an uncertainty clearly reported or absorbed into an average score?
Show where better information changed a choice and where the process still needs improvement. Do not assign precise financial benefits to avoided problems without a defensible basis.
Make Compliance Useful Before the Commitment
The future of compliance is a capability that helps leadership understand what the business can responsibly do next, what conditions apply and what evidence supports that judgement. Bring compliance into the decision while there is still a decision to shape. Speak to an XGRC® specialist about connecting compliance, management systems and assurance to your strategic decisions.