Picture a supplier selection meeting. The commercial offer is strong and the proposed service meets the need. Then the buyer asks for evidence: who can access its information, how contractors are approved, and what happens when an important control fails. The answer can change the conversation.
A promise asks the buyer to accept uncertainty. A clear explanation, supported by current evidence, gives the buyer something it can assess. That is the commercial opportunity in compliance: not a certificate used as a sales badge, and not a claim that good governance guarantees growth. Compliance becomes a competitive advantage when it helps an organisation demonstrate that it can deliver what it promises, within the conditions its customers require. The advantage is not having more compliance documents. It is being easier to trust for the right reasons.
Compliance Is a Business Capability, Not Just an Audit Event
A useful compliance programme connects applicable requirements with responsibilities, everyday work and evidence. ISO 37301 provides a management-system approach to establishing, evaluating and improving that programme, with integrity and stakeholder trust among its stated benefits. If you are still defining the scope of that capability, our guide to what GRC software is sets out how governance, risk and compliance fit together.
In commercial terms, start with three questions. What must we meet to do the work? What have we agreed to deliver? What can we demonstrate today? Keep those answers separate. An internal policy, a customer contract and a certification requirement may overlap, but they are not interchangeable, and a well-written policy does not prove that a customer-specific condition has been met. This is the gap between writing rules and running them, explored further in policy management versus governance execution.
The distinction helps commercial teams avoid selling a level of assurance that operations cannot support. It also gives operations a clearer view of the commitments the business is making on its behalf.
Why Your Customer Cares About Your Controls
For technology relationships, the buyer's assessment extends into the supplier's own practices. NIST's supply-chain guidance recommends setting requirements according to supplier criticality and specifying how acceptable security practices will be evidenced. It treats this as an ongoing relationship, not only an onboarding exercise. The commercial implication is straightforward: a supplier able to answer relevant questions with reliable evidence removes one source of uncertainty from the buying decision.
The same reasoning applies to a facilities contract or a manufacturing supply agreement. A buyer may need to understand how work is authorised, how quality problems are handled, or whether staff are competent for the task. The relevant proof will differ, so the response should be tailored rather than copied from a generic assurance pack. Ask what decision the customer is trying to make, then provide the evidence needed for that decision, without overwhelming the customer or exposing sensitive internal records.
Where the Commercial Value Can Appear
There are three places to look for value in your own business. These are mechanisms to test, not promised outcomes.
- Qualification: where a buyer specifies mandatory conditions, meeting and demonstrating them can decide whether you remain eligible
- Review effort: a maintained evidence pack can reduce repeated requests to technical, compliance and operational teams
- Delivery confidence: bringing contractual commitments into the operating process helps the delivery team understand what was promised
Extra marketing cannot substitute for an unmet entry requirement. The review-effort benefit comes from reusing reviewed information, while checking that its scope still matches the proposed service. And delivery confidence creates a basis for resolving exceptions before they become disputes at renewal.
Compliance does not replace price, service quality or product fit. It can support those strengths by making the associated commitments more credible. In a market where all credible suppliers already meet the same threshold, differentiation must come from how reliably they operate, not from claiming the threshold itself is unique.
A Certificate Helps, but Scope Still Matters
ISO describes certification as independent written assurance that specified requirements have been met, carried out by external bodies rather than by ISO itself. When presenting a certificate, check the named entity, covered activities, sites and validity, and explain how that scope relates to the service being offered. Do not let a logo imply that every product, location or customer requirement has been independently assessed.
The same discipline applies to audit summaries and testing reports. Describe what was examined, when it was examined and any material limitations. A buyer needs an accurate basis for its decision, not the broadest claim the sales team can construct. A precise statement of assurance is often more useful than an absolute claim that cannot withstand follow-up questions.
An Illustrative Supplier Decision
Consider two suppliers bidding for a multi-site service contract. This is an illustrative example, not a customer case study. Both provide a policy pack and competitive pricing. The first cannot confirm whether the same procedures operate at each proposed site: its evidence sits with individual managers, and outstanding actions are difficult to reconcile.
The second supplier shows the relevant responsibilities, training records, review results and open actions for the sites in scope. It identifies one unresolved issue, explains the interim restriction and names an accountable owner and agreed completion date.
The second supplier has not proved that nothing will go wrong. It has made its position easier to evaluate. The buyer can distinguish a controlled, disclosed exception from an unknown gap and decide whether the proposed arrangement is acceptable. That is evidence-led commercial confidence, and the benefit depends on the quality of the underlying work, not the design of the presentation.
Build an Evidence Pack That Operations Can Defend
Start with the assurance questions that recur in actual customer reviews. For each material claim, identify the responsible owner, supporting record, scope and review date. Keep open issues connected to their actions rather than hiding them in a separate tracker.
An approved response should remain linked to its source. If a service changes, a control fails or a certificate expires, the commercial explanation must be reconsidered. Reusing a once-correct answer without checking it is not efficient compliance.
Separate information suitable for public use from material that needs controlled disclosure. A high-level security statement and a detailed vulnerability report serve different audiences, so share only what is appropriate for the relationship and purpose. The IIA's Three Lines Model also distinguishes management's responsibilities from independent internal audit assurance. Commercial teams should preserve that distinction: a manager's statement and an independent assurance conclusion are different forms of evidence. Coordinating internal audit and combined assurance, as Integrated Assurance does, helps keep the two clearly labelled.
Reduce Duplication Without Weakening the Requirement
An improvement programme should examine unnecessary effort as well as missing controls. If three teams request the same training evidence, establish whether one reviewed record can support all three needs. If each business unit uses a different supplier assessment, identify which questions must be consistent and which genuinely depend on the service or risk.
Do not merge requirements merely because their wording looks similar. Check the intended outcome, covered population, frequency and evidence expected; a shared process is useful only when it satisfies each applicable purpose. This is where compliance can support margin as well as credibility: less repeated collection and reconciliation may free skilled people for assessment and improvement. Measure that effect locally rather than attaching an assumed saving to every automated task.
How XGRC® Supports Evidence-Led Compliance
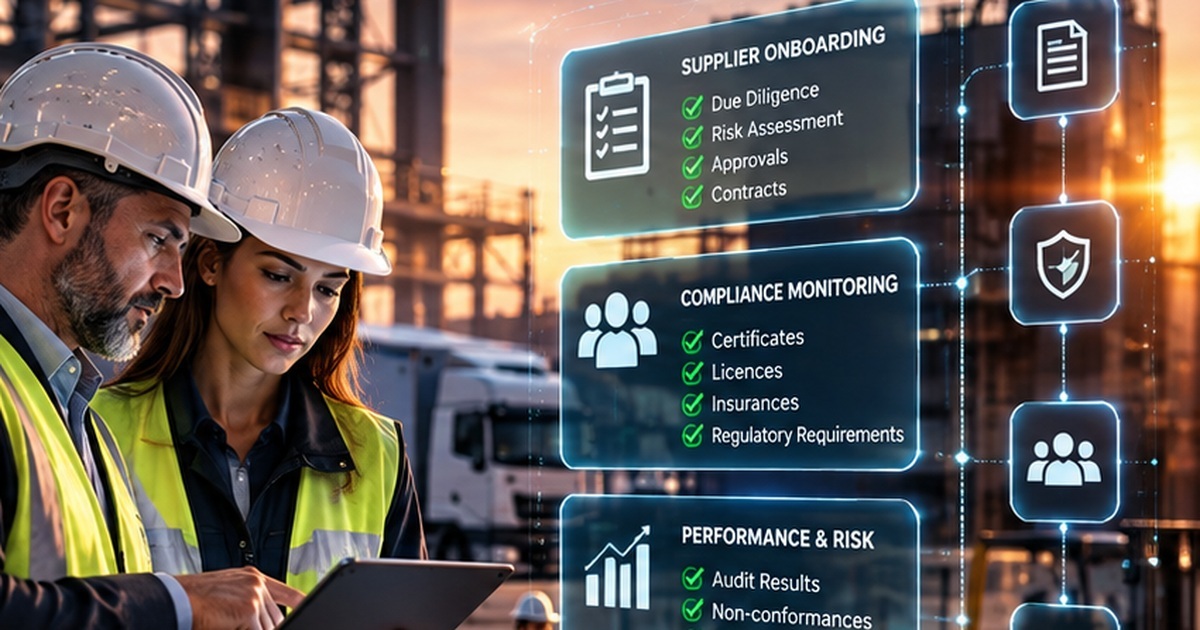
The XGRC® platform connects governance, risk, compliance and assurance records, including policies, controls, obligations, audits and corrective actions. That gives teams a shared basis for understanding what a requirement relates to and what work supports it. Turned the other way, the XGRC® Compliance Hub applies the same discipline to your own suppliers and contractors, with structured onboarding, document expiry tracking and risk scoring.
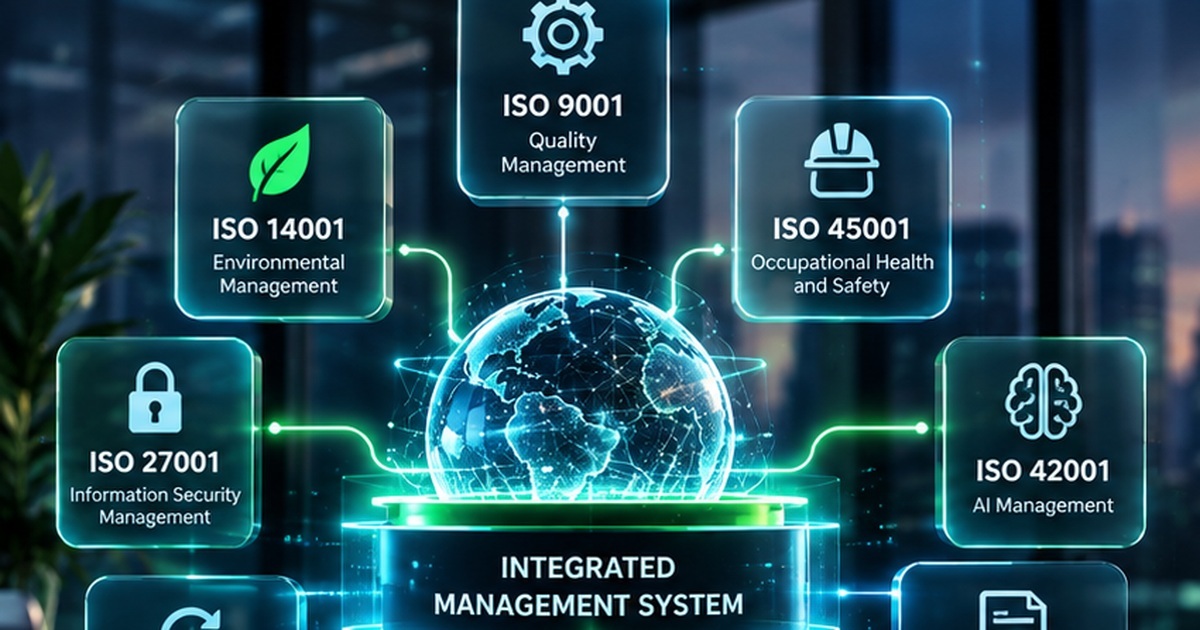
MSX® supports organisations coordinating several management disciplines through shared document control, governance workflows, audit management and performance evaluation. It offers a way to manage related activities together rather than creating a separate programme for each standard.
Apply those capabilities to a commercial requirement: connect the commitment to its owner, relevant controls and supporting records, and when a review identifies a weakness, retain the finding and the action needed to address it. The software supports the evidence and the workflow. People still need to interpret requirements, perform the work, review claims and decide what can responsibly be communicated to a customer.
Measure the Advantage Rather Than Assume It
Use a small set of measures tied to the commercial process: the time needed to answer material assurance questions, repeated evidence requests, bid delays caused by unresolved compliance gaps, and hours spent rebuilding information already held elsewhere. Pair those measures with quality checks. A faster response is not an improvement if it contains an outdated claim, and a higher qualification rate does not prove compliance caused more sales, because pricing, demand and product fit also affect the result.
Review a sample of completed opportunities with sales, operations and compliance. Ask which evidence helped, which questions exposed a genuine weakness, and what should change before the next proposal.
Make Compliance Part of the Customer Promise
Choose one important customer requirement and follow it from the proposal into delivery. Can the organisation show who owns it, how it is met and what evidence supports the answer? That is a practical place to begin. Build a repeatable response around real operating capability, then improve it as customer expectations and services change.
Trust is not created by saying the business is compliant. It is strengthened when the business can explain and demonstrate what that means. Speak to an XGRC® specialist about connecting compliance evidence with commercial and operational performance.