ISO 27001 readiness starts with knowing exactly where your ISMS stands.
XGRC® MSXCyber® gives organisations a structured way to assess ISO 27001 readiness, close control gaps, and manage the information security management system all year round, not just in the weeks before an audit.
Without continuous ISMS oversight, gaps accumulate quietly.
When asset registers, risk assessments, and Annex A controls are managed across disconnected spreadsheets, control weaknesses build up unnoticed between certification cycles — and surface as audit findings instead of managed decisions.
-
Asset inventories maintained in spreadsheets, disconnected from risk assessment
-
Control gaps only discovered when the external auditor finds them
-
Statement of Applicability out of date with the actual control environment
-
No structured evidence trail linking risks, controls, and corrective actions
The ISO 27001 implementation lifecycle, in one system.
- 01
Define ISMS scope and information security context
- 02
Run a structured gap assessment against Annex A controls
- 03
Build the asset inventory and complete risk assessment
- 04
Implement controls and complete the Statement of Applicability
- 05
Conduct internal audit against ISMS clauses and controls
- 06
Hold management review and track continual improvement
Built for information security teams, visible to management.
- Central asset register linked to risk assessment
- Configurable risk methodology aligned to ISO 27001:2022
- Statement of Applicability tracked against Annex A controls
- Incident management with regulatory disclosure tracking
- Real-time dashboards for audit and management review
 MSXCyber®
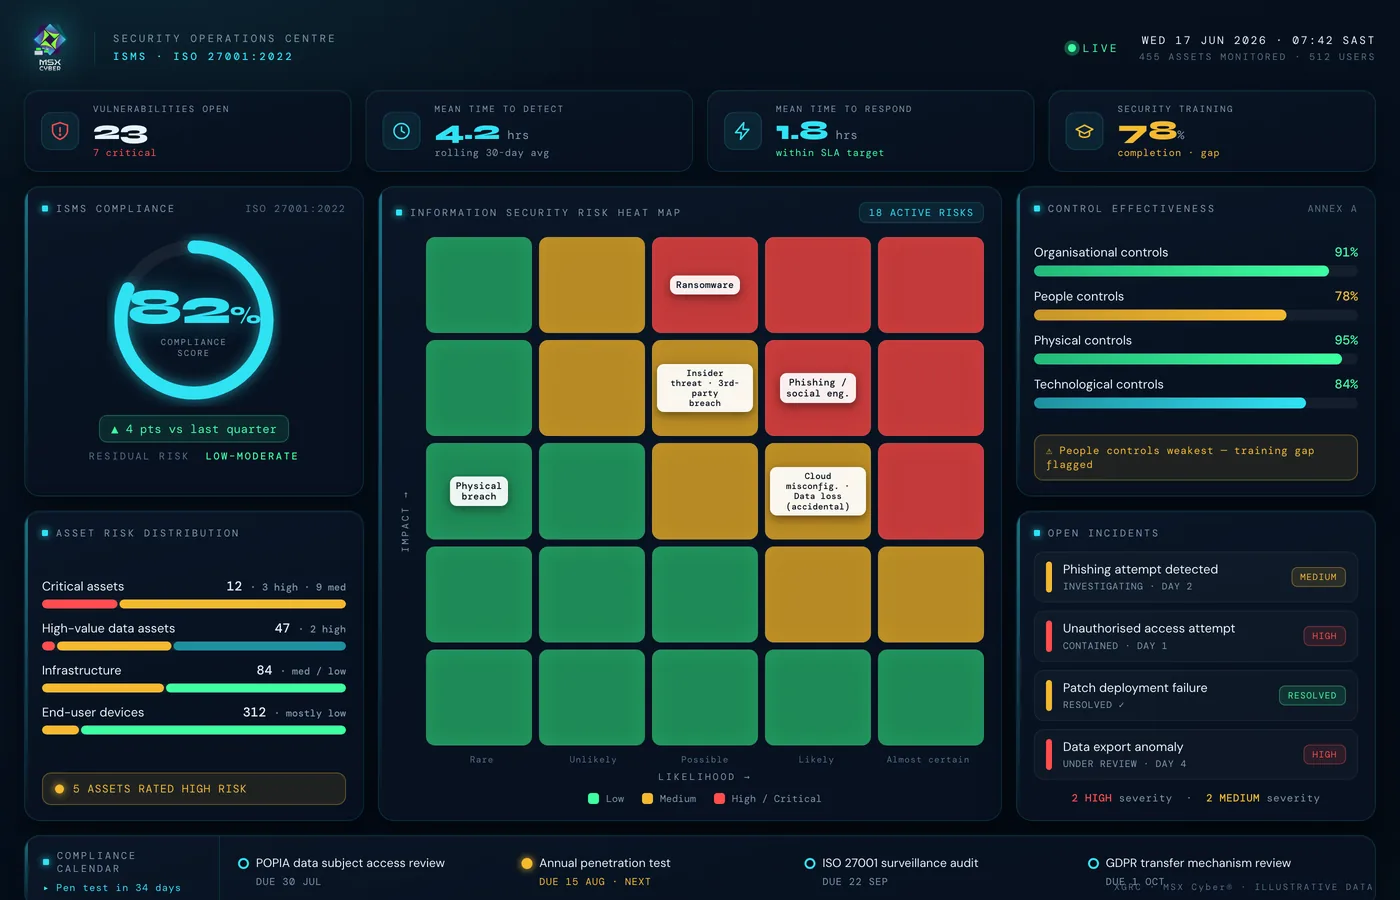
One connected view of your ISMS
MSXCyber® links the asset register, risk assessments, and Annex A controls to internal audit and incident management, so every control has a traceable evidence trail. Management gets a live view of ISMS status without waiting for the next audit cycle.
The same ISMS, without the spreadsheet chaos.
Manual approach: Asset inventories in spreadsheets
MSXCyber® approach: Centralised asset and risk register
Manual approach: Gaps found only at audit time
MSXCyber® approach: Continuous gap and control monitoring
Manual approach: Statement of Applicability out of date
MSXCyber® approach: Live Statement of Applicability
Manual approach: No linkage between risks and controls
MSXCyber® approach: Risks, controls, and actions fully linked
ISO 27001 Readiness & Gap Assessment Checklist
- Context, scope and leadership
- Risk assessment and treatment
- Annex A organisational and people controls
- Physical and technological controls
- Internal audit and management review
- Continual improvement and certification readiness
Explore the connected platform.
Solution MSXCyber®
Information Security Governance
Explore MSXCyber® → ISO Readiness ISO 27001 Documentation Checklist
What ISO/IEC 27001:2022 actually requires, what auditors expect to see, and what is worth adding once the basics are solid. Sorted into four tiers, with the clause or Annex A control for every item.
View use case → Regulatory GDPR Compliance
XGRC® gives data protection teams a structured way to manage GDPR obligations — lawful basis and consent, data subject requests, DPIAs, and breach notification — on one auditable platform, with every processing activity linked to its evidence.
View use case → Regulatory POPIA Compliance
XGRC® gives Information Officers a structured way to manage POPIA obligations on one auditable platform, including processing conditions, data subject rights, and security compromise reporting to the Information Regulator.
View use case →Common questions.
01What is ISO 27001 compliance software?
ISO 27001 compliance software assesses ISMS readiness, tracks Annex A control implementation, and manages the information security management system on an ongoing basis, rather than reconstructing evidence in the weeks before an audit.
02Does MSXCyber® keep the Statement of Applicability current?
Yes. The Statement of Applicability is tracked directly against Annex A controls as they are implemented, so it reflects the actual control environment rather than drifting out of date between audits.
03How are risks and controls linked for audit evidence?
The asset register, risk assessments and Annex A controls are linked to internal audit and incident management, so every control has a traceable evidence trail rather than scattered supporting documents.
04Which frameworks does ISO 27001 readiness align to?
ISO 27001 readiness aligns to ISO 27001:2022, ISO 27002, NIST CSF, GDPR and POPIA, reflecting how information security and data protection obligations typically overlap.
See ISO 27001 readiness as a structured, measurable process.
Book a demo to see how MSXCyber® turns ISO 27001 gap assessment, risk treatment, and control implementation into one connected, audit-ready workflow.
Where should we send your download link?
Enter your details and we will email you the link to the checklist.
Your checklist is ready.
Click the button below to download the PDF. We have also sent this link to your email.
Download the checklist (PDF)