Compliance managed through a structured external portal, not tracked through email.
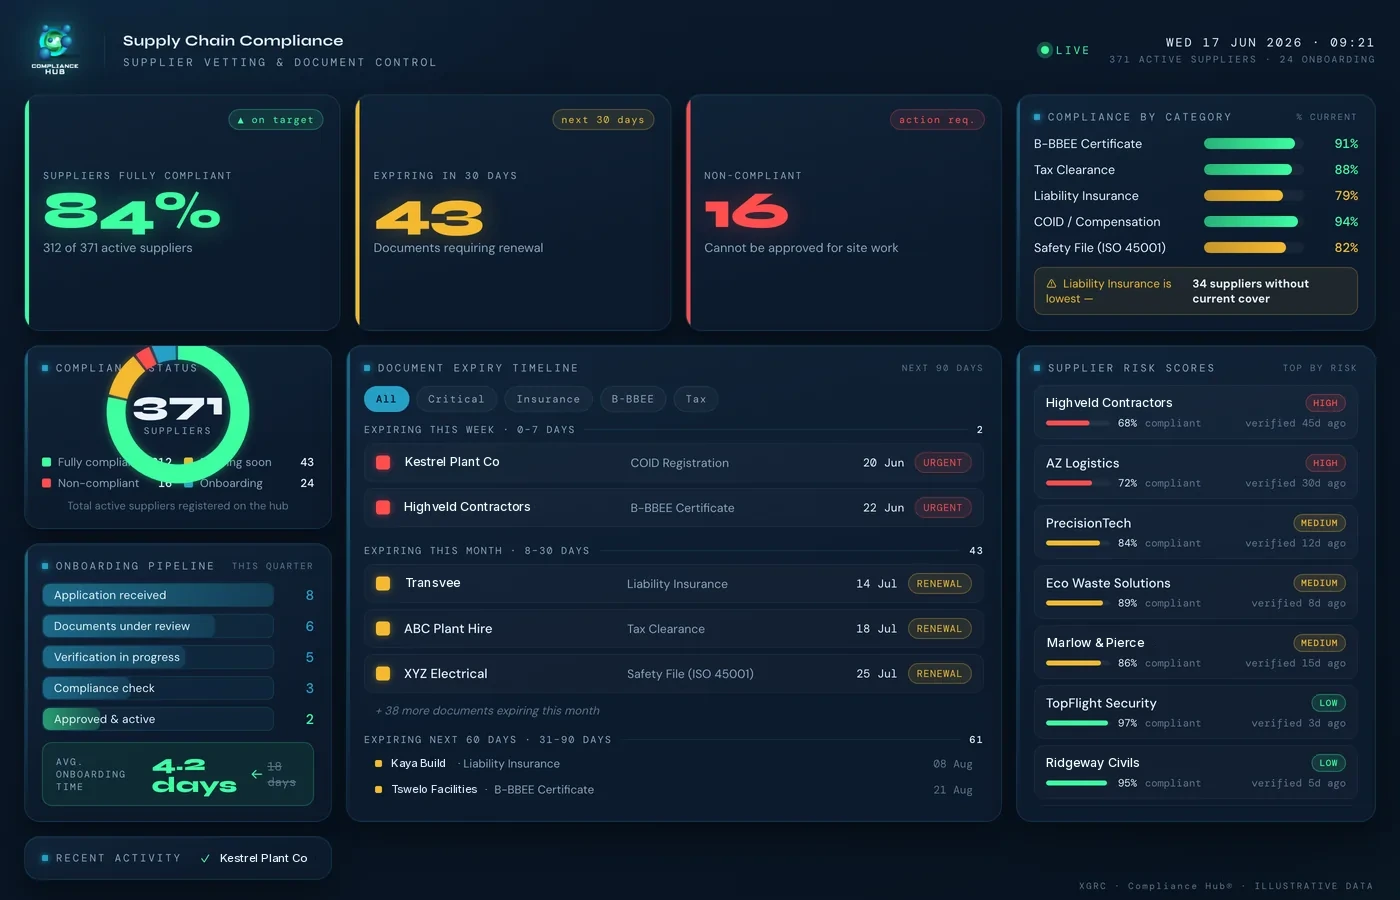
XGRC Compliance Hub enables organisations to manage supplier, contractor, and customer compliance through a structured portal. External parties upload and maintain their own documentation while internal teams validate, approve, and monitor compliance status in real time.
Unstructured third-party compliance creates risk and admin overhead.
When supplier and contractor documents are tracked by email and expiry dates are missed, internal teams carry the full burden with no reliable view of external compliance status.
-
Documents tracked via email with no central repository
-
Expiry dates not monitored — compliance lapses go unnoticed
-
High internal admin burden managing external party submissions
-
No structured onboarding process for suppliers and contractors
-
Limited visibility of third-party compliance status
A structured, portal-driven compliance process.
- 01
Define compliance requirements and structured templates
- 02
Provide portal access to external parties
- 03
External parties upload and manage their own documents
- 04
Automated expiry tracking and renewal reminders
- 05
Internal validation and approval workflows
- 06
Real-time compliance monitoring and reporting
Built for external parties, controlled by your team.
- External compliance portal for suppliers and contractors
- Structured document templates and requirements
- Document upload and management by third parties
- Automated reminders and expiry notifications
- Internal validation workflows and audit trail
- Real-time dashboards and compliance status
 XGRC® Compliance Hub
One portal. Full oversight.
XGRC Compliance Hub gives external parties a structured portal to upload and maintain their compliance documentation. Internal teams define requirements, validate submissions, track expiry dates, and monitor compliance status across all suppliers and contractors in real time.
The same compliance process, without the admin overhead.
Manual approach: Email-based document tracking
Compliance Hub approach: Portal-based compliance — shared responsibility
Manual approach: No structured onboarding process
Compliance Hub approach: Structured onboarding and templates
Manual approach: High internal admin burden
Compliance Hub approach: Automated tracking and expiry management
Compliance Hub approach: Real-time visibility across all external parties
Supplier & Contractor Compliance Checklist (ISO-aligned)
- Compliance requirement definition
- Supplier and contractor onboarding
- Document submission and validation
- Expiry and renewal management
- Monitoring and reporting
- Continuous improvement
Explore the connected platform.
Solution XGRC® Compliance Hub
Supplier & Third-Party Compliance
Explore XGRC® Compliance Hub → Use Case Vendor Management
XGRC® enables organisations to onboard, vet, and monitor suppliers and contractors through a structured process. Every vendor document, expiry date, and risk score is tracked in one place, so third-party compliance status is always known.
View use case → Use Case
Policy Management
XGRC® enables organisations to manage policies in a structured and consistent way — from development and approval through communication, acknowledgement tracking, version control, and compliance monitoring, all linked to the risks and controls they govern.
View use case → Regulatory
POPIA Compliance
XGRC® gives Information Officers a structured way to manage POPIA obligations on one auditable platform, including processing conditions, data subject rights, and security compromise reporting to the Information Regulator.
View use case →Common questions.
01What is compliance management software?
Compliance management software tracks the compliance status of suppliers, contractors and third parties in one place — requirements, document submission, expiry dates and renewals — instead of chasing paperwork by email and spreadsheet trackers.
02Does XGRC® flag expiring compliance documents automatically?
Yes. XGRC® tracks document expiry and renewal dates and can flag upcoming expirations before a supplier or contractor falls out of compliance, rather than discovering the gap during an audit.
03Can this cover both suppliers and contractors?
Yes. The same compliance requirements, onboarding and monitoring workflow applies to suppliers, contractors and other third parties, with requirements configurable per category.
04How does this connect to POPIA and data protection compliance?
Third-party compliance requirements can include data protection obligations under POPIA, so supplier and contractor compliance status and data protection compliance are tracked on the same platform rather than in separate systems.
See compliance management as a structured, portal-driven process.
Book a demo to see how XGRC Compliance Hub enables structured, scalable compliance across external stakeholders.
Where should we send your download link?
Enter your details and we will email you the link to the checklist.
Your checklist is ready.
Click the button below to download the PDF. We have also sent this link to your email.
Download the checklist (PDF)