Every SHEQ management system depends on information, and most of that information starts with an incident report. A worker slips on a wet walkway, a forklift clips a racking upright, a drum leaks into a stormwater drain, a batch fails a quality check. What happens next, whether the event is investigated, whether the cause is found, whether anything changes, depends almost entirely on whether it was reported, how quickly, and how well. Incident reporting is not an administrative step at the end of an event. It is the input every other SHEQ process relies on.
What Counts as an Incident in SHEQ
In a SHEQ context, an incident is broader than an injury. Most organisations capture several categories, each of which feeds a different part of the management system:
- Injuries and occupational illnesses, from first aid cases to serious and fatal injuries
- Near misses, where harm could have occurred but did not
- Dangerous occurrences, such as uncontrolled releases, equipment failures or structural collapses
- Environmental incidents, such as spills, emissions, uncontrolled discharges or waste handling failures
- Quality incidents and non-conformances, where a product, service or process fails to meet requirements
- Property and equipment damage, which often signals a control that is not working
A SHEQ approach captures all of these in one place, because the same event frequently falls into more than one category. For a broader view of how the four disciplines fit together, see what is SHEQ.
Why Incident Reporting Is Critical
Incident reporting matters for reasons that go well beyond keeping a record:
- It is a legal obligation. Certain incidents must be reported to the authorities, and failing to do so is an offence in its own right
- It is how the organisation learns. An incident that is not reported cannot be investigated, and a cause that is not found will usually recur
- It drives corrective action. Every corrective and preventive action in the system should trace back to something that was reported, inspected or audited
- It informs risk assessment. Incident trends show where existing controls are not working and where risk assessments need revisiting
- It is audit evidence. ISO certification bodies, inspectors and clients expect to see incidents reported, investigated and closed, not just logged
- It reflects and shapes culture. The number and quality of reports tell leadership a great deal about whether people trust the system and feel safe raising concerns
The Legal Side of Incident Reporting in South Africa
South African legislation places specific reporting duties on employers. Section 24 of the Occupational Health and Safety Act 85 of 1993 requires certain incidents to be reported to an inspector, including incidents in which a person dies, is seriously injured or becomes ill, major incidents, and specified dangerous occurrences such as the spillage of a dangerous substance or the uncontrolled release of a substance under pressure. The regulations under the Act set out how and when these reports must be made, and the employer is expected to record and investigate incidents, not simply notify them.
Other legislation adds its own obligations. Workplace injuries and occupational diseases are reported for compensation purposes under the Compensation for Occupational Injuries and Diseases Act 130 of 1993. Mines report under the Mine Health and Safety Act 29 of 1996. Section 30 of the National Environmental Management Act 107 of 1998 deals with the reporting and control of emergency environmental incidents. Which obligations apply depends on the sector and the site, and the specific regulations should always be checked, but the common thread is clear: organisations need a reliable way to know about every incident quickly, classify it correctly and show what they did about it. The wider local context is covered on the SHEQ software in South Africa page.
What ISO 45001, ISO 14001 and ISO 9001 Expect
All three standards include requirements for dealing with incidents and non-conformities. ISO 45001 goes furthest: it requires a process to report, investigate and act on incidents and nonconformities, and among top management's leadership commitments it includes protecting workers from reprisals when they report incidents, hazards, risks and opportunities. ISO 14001 and ISO 9001 both require organisations to react to non-conformities, determine their causes, take corrective action and review whether that action was effective. In each case, the standard assumes reporting is happening. If it is not, the rest of the clause cannot be met.
Why Near Misses Matter Most
Near misses are the most valuable and the most under-reported incidents. By definition, nobody was hurt, nothing was spilled and no product was lost, so there is little pressure to report. Yet a near miss is a free lesson: the hazard is real, the control has failed or nearly failed, and the organisation has the chance to fix it before the outcome is worse. Near misses also tend to be far more frequent than serious incidents, which makes them one of the richest sources of preventive information a SHEQ team has. A rising near miss reporting rate is often a sign of a healthier reporting culture, not a more dangerous workplace. The patterns near misses reveal, when they are connected to inspections, findings and overdue actions, are explored in why SHEQ incidents are often a data problem.
Why Incident Reporting Breaks Down
When reporting rates are low, the cause is rarely that nothing is happening. More often, reporting is simply harder than staying quiet:
- Paper forms that have to be found, filled in and handed in, often at the end of a long shift
- Long, complicated forms designed for the investigation rather than the first report
- A culture where reporting leads to blame rather than improvement
- No feedback, so people report once, see nothing change and stop reporting
- No clear route for contractors and visitors to report
- Reports sent by email or WhatsApp that never reach a central record
Each of these can be fixed, but only if the organisation treats reporting as something to design deliberately rather than assume.
What Makes an Incident Report Useful
A good first report is quick to submit and captures enough to act on. The investigation can add detail later. At minimum, a useful report records:
- What happened, where and when
- Who was involved or affected, including contractors and members of the public
- The immediate actions taken to make the area safe or contain the event
- An initial severity classification, so the right people are notified and legal reporting duties are identified
- Supporting evidence such as photos, documents or witness details
From there, the report should move into a structured process: an investigation proportionate to the severity, a root cause rather than just an immediate cause, corrective and preventive actions assigned to named owners with due dates, and verification that those actions actually resolved the cause before the incident is closed.
From Report to Closed Loop
The value of incident reporting is only realised when the loop is closed. A report that sits in a register with no investigation, no action and no verification teaches the organisation nothing and tells the reporter their effort was wasted. A closed loop connects the report to the investigation, the investigation to the root cause, the root cause to corrective actions, the actions to verified closure, and the lessons back into risk assessments, procedures and training. This is the structured incident process described in the incident management use case, and it depends on the same discipline set out in action management: actions with owners, deadlines and evidence, tracked until they are genuinely complete.
Incident Reporting Across Multiple Sites
For organisations with several sites, the value of incident reporting multiplies when reports are captured the same way everywhere. If every site uses the same classifications and severity ratings, a group SHEQ manager can see that three sites have reported similar near misses involving the same activity, and act across the group before one of them becomes a serious incident. If each site uses its own form and its own spreadsheet, that pattern stays invisible. Consistent, group-wide reporting is one of the main reasons organisations consolidate their SHEQ systems, as covered in how to consolidate SHEQ management across multiple sites.
How SHEQX® Supports Incident Reporting
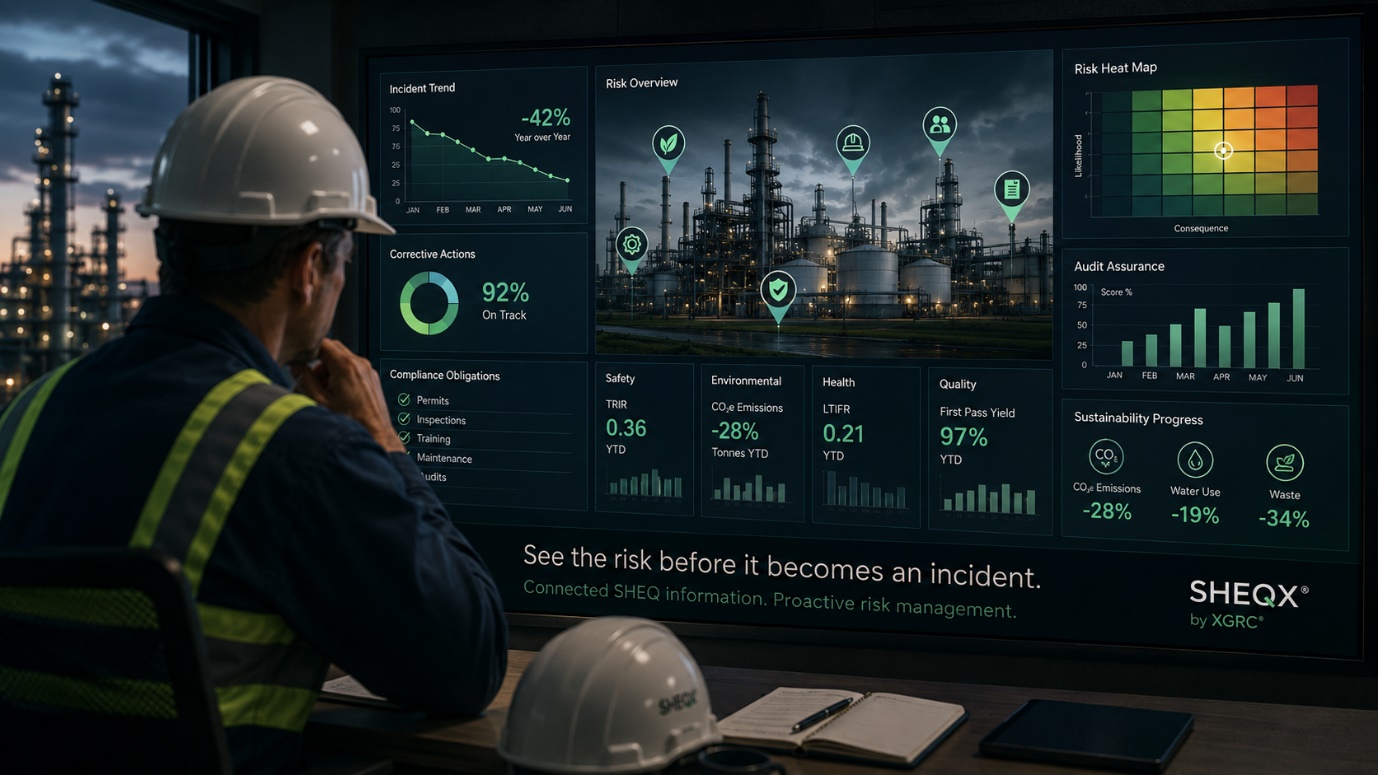
SHEQX® by XGRC® Software is built to make incidents easy to report and hard to lose. It provides mobile-friendly incident capture with photo and document evidence, configurable severity classification and escalation rules, structured root cause analysis workflows, automated corrective action assignment and tracking, and real-time dashboards on incident trends and open actions. Every incident links to its investigation, root cause and corrective actions, and connects to the risk register and audit findings, so leadership sees not only what happened but whether it was actually resolved. Across the scope of a SHEQ function, that covers safety incidents and near misses, environmental incidents and quality nonconformities on one platform, aligned to ISO 45001, ISO 14001 and ISO 9001. Incident reporting is one part of a wider SHEQ system; for the full picture, see what SHEQ software does across safety, health, environment and quality.