ISO 31000 gives risk management its structure. XGRC® gives it a system.
ISO 31000 is a guideline for managing risk, not a certifiable management system — there is no audit to pass. XGRC® helps organisations adopt and embed the ISO 31000 risk management process, from establishing context through risk assessment, treatment, and ongoing monitoring and review.
Without a structured process, risk management becomes a compliance exercise.
When context, criteria, and treatment are not applied consistently, risk registers drift out of date and stop reflecting the organisation's actual exposure — which is exactly what the ISO 31000 process is designed to prevent.
-
Risk management run as an annual exercise rather than a continuous process
-
No consistent criteria for likelihood, impact, or risk appetite across business units
-
Risk treatment actions assigned but never checked for effectiveness
-
Risk reporting disconnected from real decision-making forums
The ISO 31000 risk management process, in one system.
- 01
Establish the internal and external context and risk criteria
- 02
Identify risks across strategic, operational, financial and compliance categories
- 03
Analyse likelihood and consequence using a consistent scoring model
- 04
Evaluate risks against risk appetite and prioritise treatment
- 05
Define and assign risk treatment plans with clear ownership
- 06
Monitor, review and report on risk performance continuously
Built for risk owners, visible to the board.
- Central risk register aligned to the ISO 31000 process
- Configurable risk criteria and appetite thresholds
- Risk treatment plans with owner and effectiveness tracking
- Key risk indicator monitoring and escalation
- Real-time dashboards and board-ready reporting
 Enterprise Risk Management
One connected view of risk
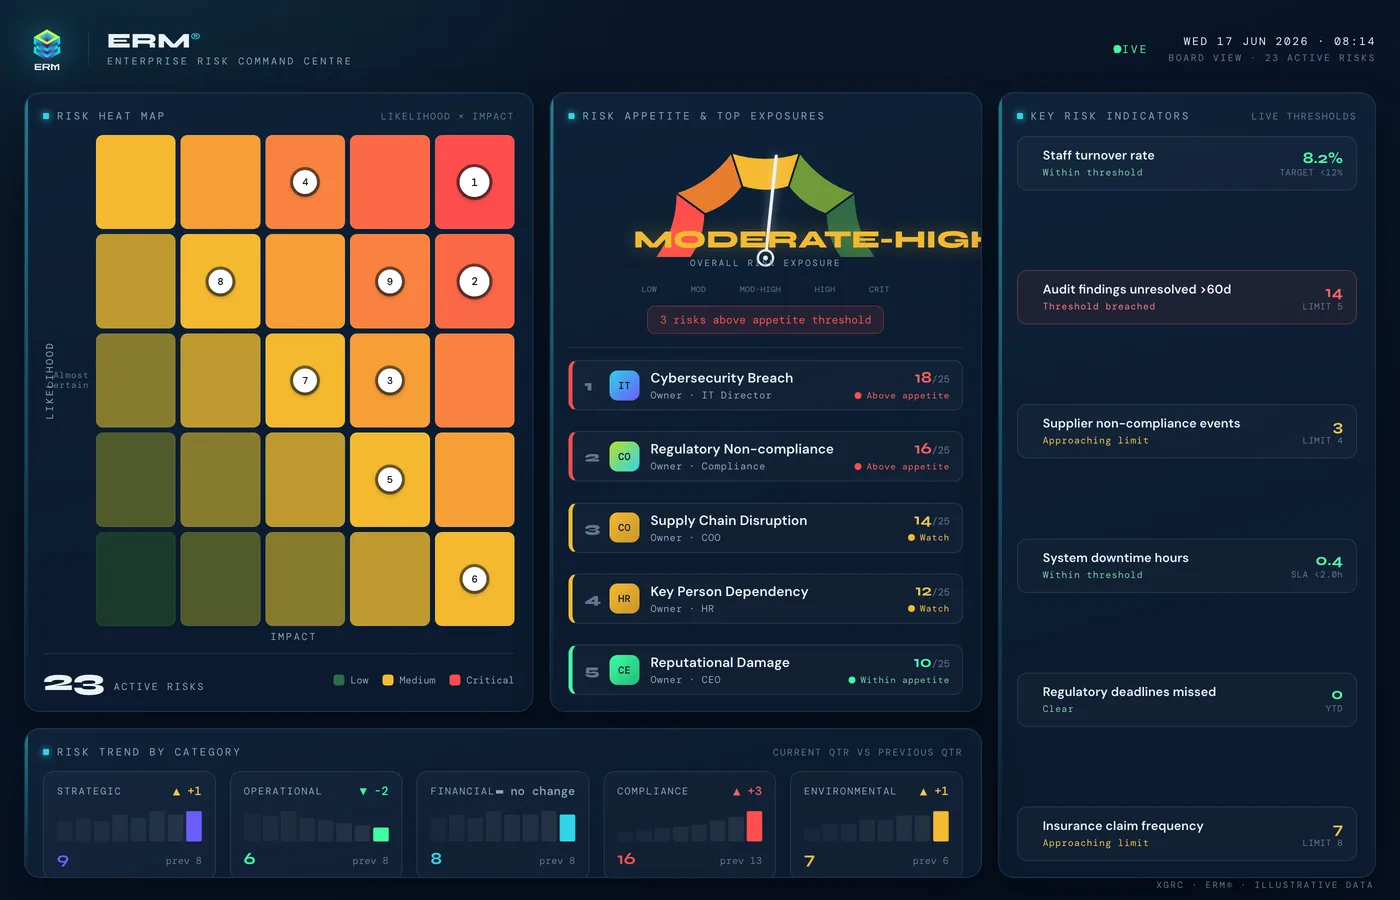
XGRC® structures risk identification, analysis, evaluation and treatment around the ISO 31000 process, and links every risk to its controls, actions and audit findings. The board gets real-time visibility of risk exposure without waiting for the next review cycle.
The same risk process, without the friction.
Manual approach: Risk management as an annual, point-in-time exercise
XGRC® approach: Continuous risk identification and review
Manual approach: Inconsistent criteria across business units
XGRC® approach: Consistent context, criteria and appetite thresholds
Manual approach: Treatment actions never checked for effectiveness
XGRC® approach: Treatment tracked through to verified effectiveness
Manual approach: Reporting disconnected from decision-making
XGRC® approach: Risk reporting embedded in governance forums
ISO 31000 Risk Management Checklist
- Principles and mandate
- Framework design
- Establishing the context
- Risk assessment — identification, analysis and evaluation
- Risk treatment
- Monitoring, review, recording and reporting
Explore the connected platform.
Solution Enterprise Risk Management
Enterprise Risk Intelligence
Explore Enterprise Risk Management → Use Case Risk Management
XGRC® is risk management software that lets organisations identify, assess and manage risks in a structured, consistent way. It connects risks to controls, actions and assurance activities on a single platform, giving clear visibility of risk exposure across the organisation.
View use case → Use Case Enterprise Risk Management
XGRC® provides a central ERM platform aligned to ISO 31000, COSO, and King V. Define your risk framework, identify and assess risks across all categories, link every risk to controls and audit findings, and report to the board with real-time visibility.
View use case → Regulatory
King V Governance
XGRC® gives boards and governance teams a structured way to apply King V principles and report on them with evidence — risk governance, combined assurance, and ESG oversight — on one auditable platform. King V is South Africa's corporate governance code, applied on an apply-and-explain basis: it is governance best practice organisations are expected to report against, not a certifiable legal requirement.
View use case → Use Case Risk Register Template
Most organisations start their risk register in a spreadsheet. It works until a second risk owner edits it, a rating changes with no record of why, or the board asks for a rollup that takes three days to compile. This checklist sets out the fields and structure a risk register actually needs — the same structure XGRC® ERM runs live, with an audit trail built in.
View use case →Common questions.
01What is ISO 31000 risk management software?
ISO 31000 is a guideline for managing risk, not a certifiable standard, so there is no audit to pass. XGRC® software helps organisations adopt and embed the ISO 31000 process, from establishing context through risk assessment, treatment and ongoing review.
02Does XGRC® apply consistent risk criteria across business units?
Yes. Risk criteria and appetite thresholds are configurable once and applied consistently, so likelihood and impact are scored the same way regardless of which business unit raises the risk.
03Is risk treatment checked for effectiveness, not just assigned?
Yes. Risk treatment plans are tracked with owner and effectiveness monitoring, so a treatment is verified to have actually reduced the risk rather than assumed complete once assigned.
04How does this connect to COSO ERM and King V?
The ISO 31000 process underpins COSO ERM and King V risk governance requirements, so the same risk register and reporting feed all three without maintaining separate risk frameworks.
See ISO 31000 as a structured, embedded risk process.
Book a demo to see how XGRC® turns the ISO 31000 risk management process — context, assessment, treatment and review — into one connected workflow.
Where should we send your download link?
Enter your details and we will email you the link to the checklist.
Your checklist is ready.
Click the button below to download the PDF. We have also sent this link to your email.
Download the checklist (PDF)