Enterprise risk management embedded in governance — not tracked in spreadsheets.
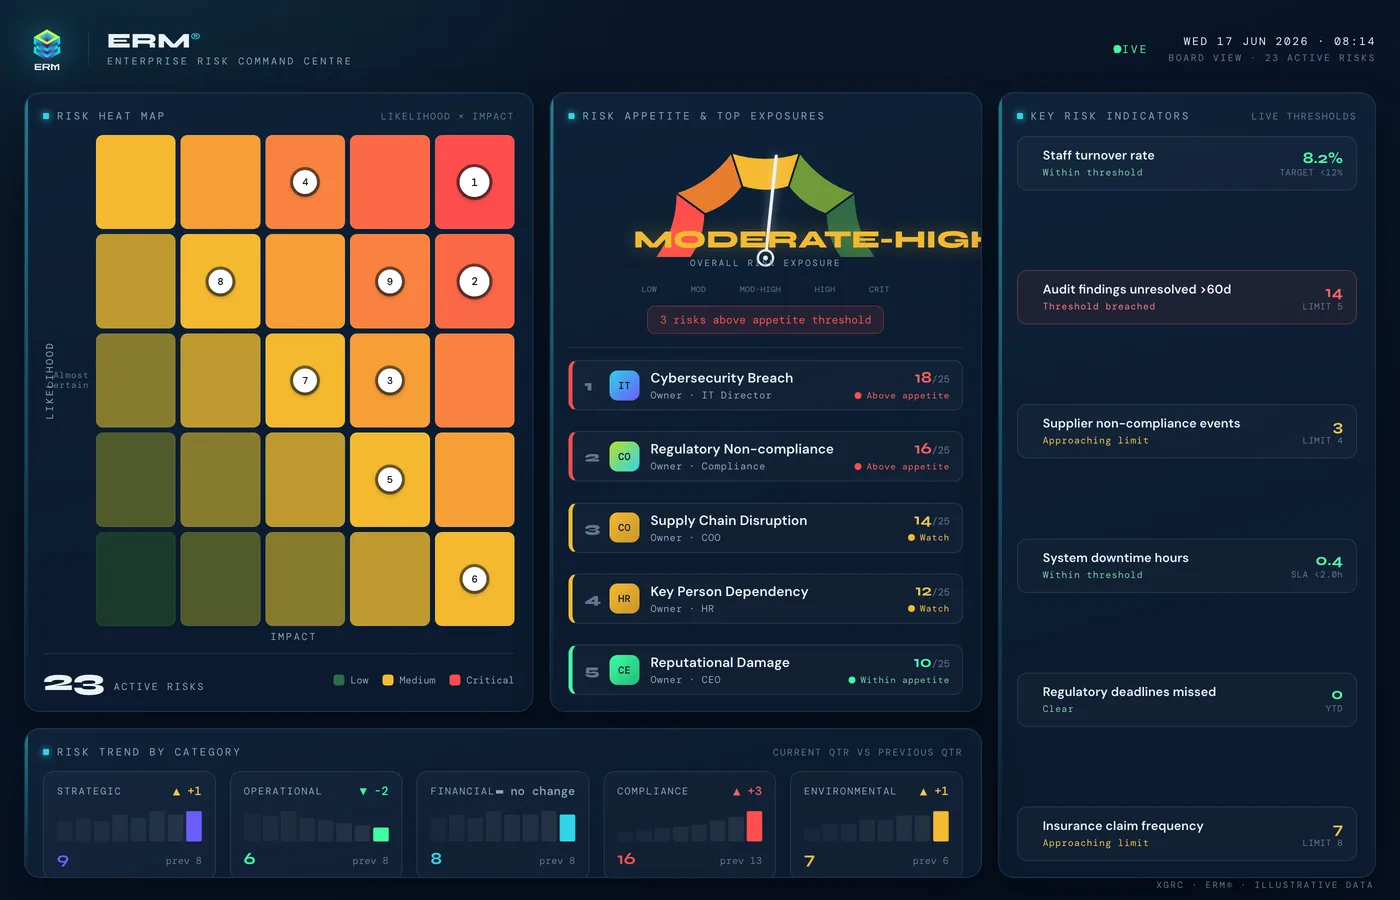
XGRC® provides a central ERM platform aligned to ISO 31000, COSO, and King V. Define your risk framework, identify and assess risks across all categories, link every risk to controls and audit findings, and report to the board with real-time visibility.
Fragmented risk management creates blind spots across the organisation.
When risk registers live in spreadsheets and scoring is inconsistent across teams, leadership cannot see the true risk exposure of the organisation.
-
Fragmented risk registers across business units
-
Inconsistent scoring methodology and risk appetite definitions
-
Limited visibility of risk exposure for leadership
-
Poor linkage between risks, controls, and audit findings
A structured, repeatable risk management process.
- 01
Define risk management framework and governance structure
- 02
Identify risks across strategic, operational, financial and compliance dimensions
- 03
Assess likelihood and impact using a consistent scoring model
- 04
Define and assign risk treatment plans with clear ownership
- 05
Monitor risk indicators and escalate critical exposures
- 06
Report risk status to management and the board
Built for risk owners. Visible to leadership.
- Central risk register with consistent taxonomy
- Configurable scoring models and risk appetite thresholds
- Risk appetite and tolerance tracking
- Integration with controls, audits, and compliance obligations
- Real-time dashboards and board-ready reporting
 Enterprise Risk Management
One connected view of risk
XGRC® centralises the risk register, links risks to controls and internal audits, and provides real-time dashboards for leadership. Risk owners get structured workflows and action tracking. The board gets complete visibility without waiting for manual reports.
The same risk process, without the manual overhead.
Manual approach: Spreadsheet-based risk tracking
XGRC® approach: Structured, centralised risk register
Manual approach: Inconsistent scoring across departments
XGRC® approach: Consistent framework and scoring model
Manual approach: Manual, periodic reporting
XGRC® approach: Real-time dashboards and automated reporting
Manual approach: No linkage to controls or audit
XGRC® approach: Risks linked to controls, audits, and compliance
Enterprise Risk Management Checklist (ISO 31000 / COSO aligned)
- Governance & risk framework
- Risk identification across all categories
- Risk assessment and scoring
- Risk treatment and action tracking
- Monitoring, escalation and review
- Reporting, integration and continuous improvement
Explore the connected platform.
Solution Enterprise Risk Management
Enterprise Risk Intelligence
Explore Enterprise Risk Management → Use Case Risk Management
XGRC® is risk management software that lets organisations identify, assess and manage risks in a structured, consistent way. It connects risks to controls, actions and assurance activities on a single platform, giving clear visibility of risk exposure across the organisation.
View use case → Use Case
Integrated Assurance
XGRC® coordinates internal audit and combined assurance across your organisation, linking every finding to the risk it relates to and the controls meant to manage it. Every line of defence works from the same assurance map.
View use case → ISO Readiness ISO 31000 Risk Management
ISO 31000 is a guideline for managing risk, not a certifiable management system — there is no audit to pass. XGRC® helps organisations adopt and embed the ISO 31000 risk management process, from establishing context through risk assessment, treatment, and ongoing monitoring and review.
View use case → Use Case Risk Register Template
Most organisations start their risk register in a spreadsheet. It works until a second risk owner edits it, a rating changes with no record of why, or the board asks for a rollup that takes three days to compile. This checklist sets out the fields and structure a risk register actually needs — the same structure XGRC® ERM runs live, with an audit trail built in.
View use case → Use CaseAI Governance Readiness
Two laws now sit behind AI governance: ISO/IEC 42001 certifies your organisation's AI management system, and the EU AI Act regulates each AI system individually. This checklist covers what both actually require, so a readiness gap is something you find on your own terms, not an auditor's.
View use case →Common questions.
01What is enterprise risk management (ERM) software?
ERM software gives leadership a single, board-ready view of risk exposure across the whole organisation, aligned to a defined framework such as ISO 31000, COSO or King V, rather than risk being managed inconsistently by department.
02How does XGRC® support King V governance requirements?
XGRC® aligns risk identification, assessment and reporting to King V governance principles, giving the board visibility of risk appetite, exposure and treatment status in the format governance committees expect.
03What is the difference between this and the Risk Management use case?
Risk Management covers day-to-day operational risk identification and control at team level. Enterprise Risk Management adds the governance layer on top — a defined risk framework, board reporting and escalation across strategic, operational, financial and compliance categories.
04Can XGRC® link risks to audit findings automatically?
Yes. Every risk can be linked to its controls and to related audit findings, so a control weakness identified in audit automatically informs the residual risk score for the risk it relates to.
See how XGRC® enables structured enterprise risk management.
Book a demo to see how XGRC® enables structured ERM — from risk identification and assessment through to board-level reporting.
Where should we send your download link?
Enter your details and we will email you the link to the checklist.
Your checklist is ready.
Click the button below to download the PDF. We have also sent this link to your email.
Download the checklist (PDF)