ISO/IEC 42001 readiness starts with an AI management system that runs, not a policy that sits.
ISO/IEC 42001 certifies the management system around your AI: the policy, the owners, the risk and impact assessments, the controls and the audits that keep it honest. XGRC® AI Governance runs that system all year, so a certification audit tests what is already in place.
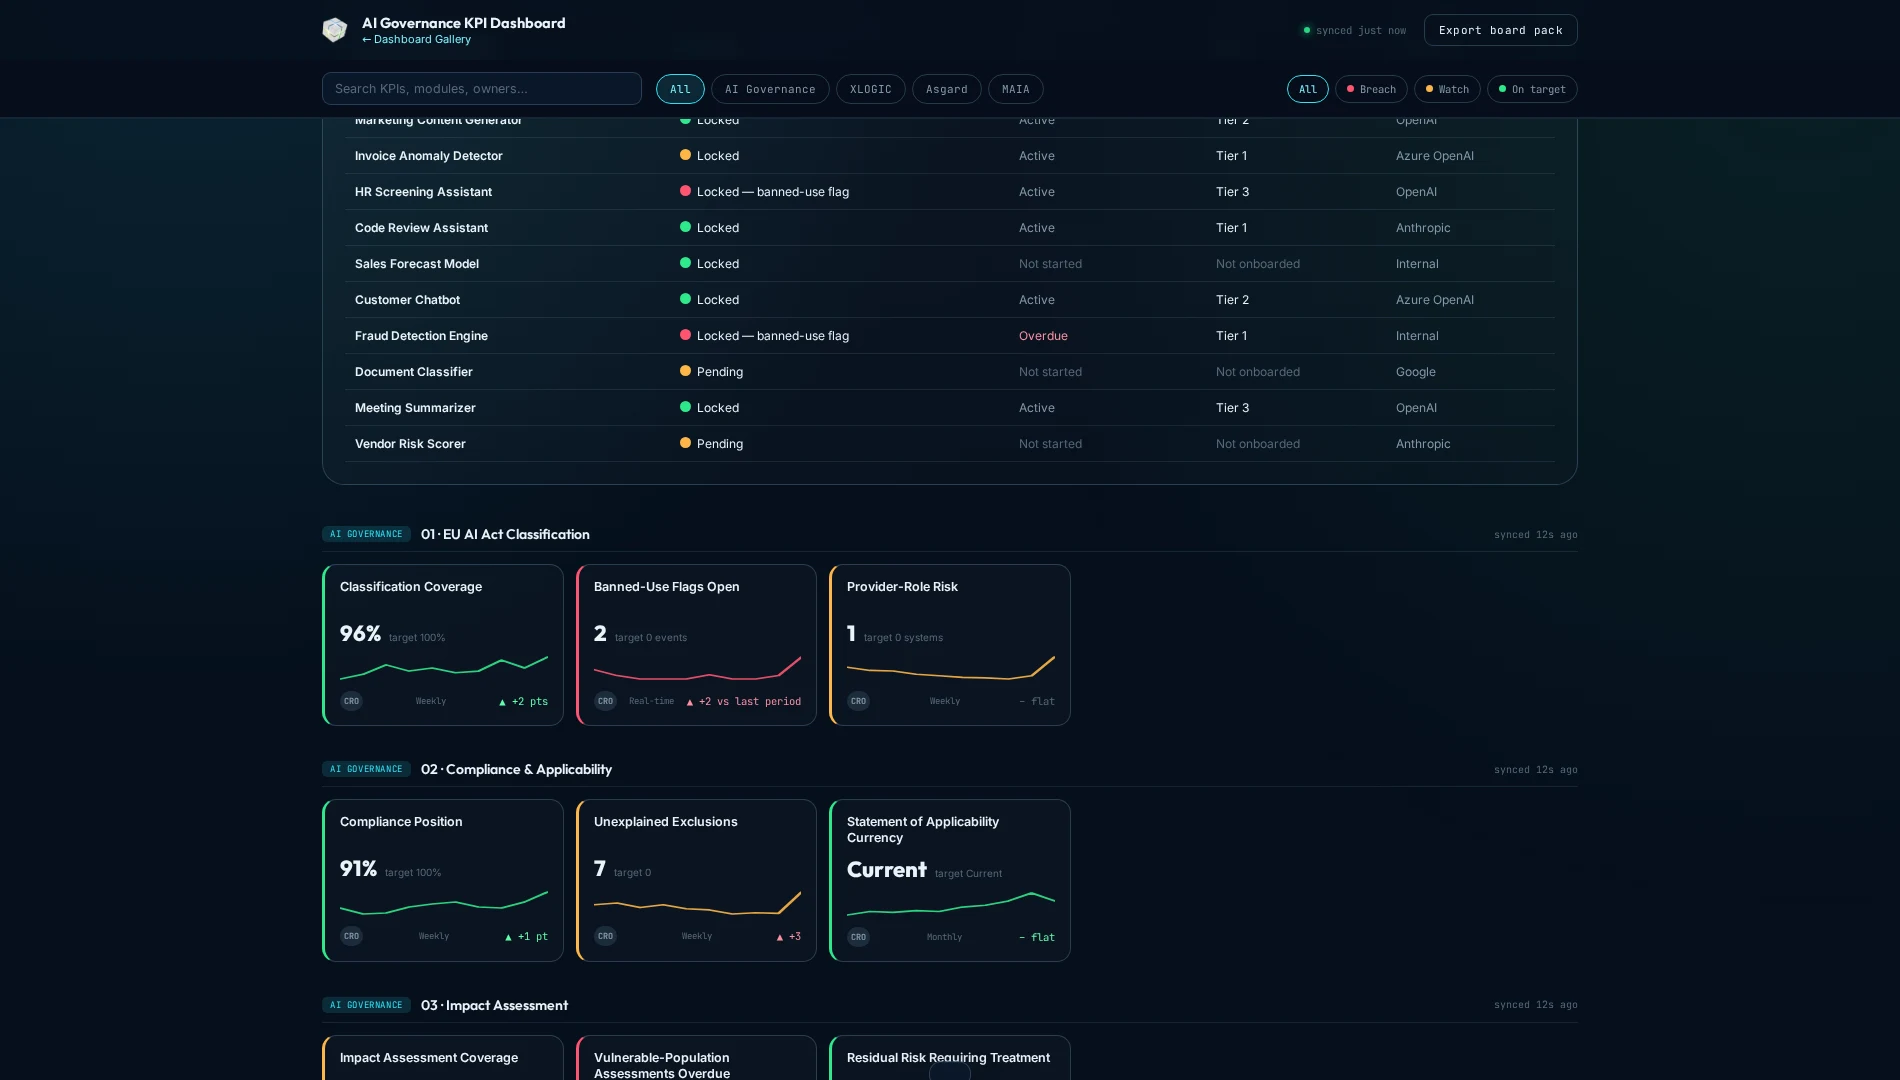
Auditors do not certify intentions. They test a working system.
Most organisations starting ISO/IEC 42001 have good AI practices in pockets. What is usually missing is the management system that ties them together: a defined scope, an AI risk and impact process that repeats, controls chosen for a reason and evidence that the whole thing is reviewed.
-
An AI policy exists, but no scope, objectives or named owners behind it
-
AI risk and impact assessed once for a project, then never revisited
-
No Statement of Applicability, or one that no longer matches the controls in place
-
Internal audit and management review not yet run on the AI management system
The ISO/IEC 42001 lifecycle, in one system.
- 01
Define the context and scope of the AI management system, including your role for each AI system
- 02
Set the AI policy, objectives and accountable roles, with top management commitment
- 03
Run AI risk assessment, risk treatment and AI system impact assessment as repeatable processes
- 04
Select Annex A controls and record each one applied or excluded, with reasons, in the Statement of Applicability
- 05
Operate the controls across the AI system life cycle, with evidence attached
- 06
Run internal audit and management review, and close nonconformities through corrective action
Built for the people who will stand in front of the auditor.
- An AI management system module with policy, objectives, roles, competence and internal audit
- Starter content for ISO/IEC 42001 that your team adopts and maintains as its own
- A Statement of Applicability generated from the controls you actually apply
- One control library mapped once across ISO/IEC 42001, the EU AI Act, GDPR and POPIA
- A twelve-step setup wizard and a ready check that shows what is in place and what still needs attention
 AI Governance
A management system on top of every AI system
The ISO/IEC 42001 management system in XGRC® AI Governance sits above the AI system records. Classification, impact, risk, controls, oversight, incidents and change all feed it, so management review sees real performance, not a summary prepared for the audit.
The same standard, without the binder.
Manual approach: AI policy in a shared folder
AI Governance approach: Policy, objectives and owners in one system
Manual approach: Risk and impact assessed per project, then forgotten
AI Governance approach: Repeatable risk and impact assessments per AI system
Manual approach: Statement of Applicability rebuilt before each audit
AI Governance approach: Statement of Applicability kept live from applied controls
Manual approach: Internal audit planned when the auditor is booked
AI Governance approach: Internal audit and management review on a schedule
ISO/IEC 42001 Readiness & Gap Assessment Checklist
- Context, scope and interested parties
- Leadership, AI policy and roles
- AI risk assessment, treatment and impact assessment
- Support, competence and documented information
- Annex A controls and the Statement of Applicability
- Internal audit, management review and improvement
Explore the connected platform.
Solution AI Governance
Govern every AI system, from register to regulator: EU AI Act classification, ISO/IEC 42001 readiness, GDPR and POPIA compliance, risk, incidents and oversight in one workspace inside XGRC®.
Explore AI Governance → Use Case AI Governance Readiness
Two laws now sit behind AI governance: ISO/IEC 42001 certifies your organisation's AI management system, and the EU AI Act regulates each AI system individually. This checklist covers what both actually require, so a readiness gap is something you find on your own terms, not an auditor's.
View use case → Regulatory EU AI Act Compliance
The EU AI Act regulates AI system by system. Your duties depend on what each system does, where it is used and whether you built it or deploy it. XGRC® AI Governance records that decision for every system, scopes the obligations that follow and keeps the evidence that you meet them.
View use case → ISO Readiness
ISO 27001 Readiness
XGRC® MSXCyber® gives organisations a structured way to assess ISO 27001 readiness, close control gaps, and manage the information security management system all year round, not just in the weeks before an audit.
View use case →Common questions.
01What is ISO/IEC 42001?
ISO/IEC 42001 is the international standard for an AI management system. It sets out how an organisation governs the AI it develops, provides or uses: policy, roles, AI risk and impact assessment, controls across the AI life cycle, and audit and review. It follows the same clause structure as ISO 27001 and ISO 9001.
02Does XGRC® certify us for ISO/IEC 42001?
No tool certifies you; only an accredited certification body can. XGRC® gives you the AI management system, the evidence and the Statement of Applicability an auditor looks for.
03What is the Statement of Applicability in ISO/IEC 42001?
It lists the Annex A controls, states whether each one is applied or excluded and gives the reason. It is usually the first document a certification auditor asks for, so it has to match the controls actually in place.
04We already have ISO 27001. How much can we reuse?
A lot. ISO/IEC 42001 shares the same clause structure, so document control, internal audit, management review and corrective action can follow the same processes. What is new is AI-specific: AI system impact assessment, AI risk sources and the Annex A controls for data and the AI life cycle.
See ISO/IEC 42001 readiness as a system you run, not a project you finish.
Book a demo to see the AI management system, Statement of Applicability and mapped control library working together in XGRC® AI Governance.
Where should we send your download link?
Enter your details and we will email you the link to the checklist.
Your checklist is ready.
Click the button below to download the PDF. We have also sent this link to your email.
Download the checklist (PDF)